

SAVYINT and Kryptus Advance Secure Payments with Digital Identity, Tokenization and HSM Technology
As digital payments, Open Banking and Digital Wallets continue to evolve rapidly, payment security is no longer limited to protecting card data. Financial institutions need a comprehensive security architecture that provides end-to-end protection – from user identity, authentication and transactions to cryptographic keys, payment data and API connectivity. SAVYINT and Kryptus are working together to combine complementary capabilities in Payment HSM, Payment Tokenization, Digital Identity, Strong Authentication, Transaction Signing and Secure API, with the goal of building a Secure Payment Infrastructure for banks, digital wallets, Fintechs and digital payment ecosystems. Under the partnership framework, Payment Tokenization has been identified as one of the key use cases, alongside Government Digital Identity & Digital Signing. This approach is designed to extend cryptographic protection and Digital Trust capabilities from the infrastructure layer to high-value digital financial transactions that require robust security, control and scalability. Comprehensive Security Across the Entire Transaction Lifecycle A digital payment transaction today can involve multiple components, including user identity, authentication mechanisms, banking or digital wallet applications, APIs, payment processing systems, card data, cryptographic keys and third-party services. As ecosystems become increasingly interconnected, a vulnerability at any layer can potentially affect the security of the entire transaction. Payment security therefore needs to be designed as an end-to-end chain of trust, rather than focusing solely on individual components. In the architecture envisioned by SAVYINT and Kryptus, the protection chain consists of: Digital Identity, Strong Authentication, Transaction Signing, Tokenization, HSM & Key Protection, Secure API, Audit & Compliance. This approach connects Identity Trust with Cryptographic Trust and Payment Trust, creating the foundation for a secure and scalable digital payment architecture. Payment Tokenization – A Key Focus of the Partnership The growth of Apple Pay, Android Wallet, Digital Wallets, mobile payments and card-on-file services is transforming the way users store and make payments. In this model, Payment Tokenization plays an important role in reducing direct exposure to sensitive payment data. Instead of using original payment data throughout transaction flows, tokens can be used in appropriate, controlled contexts and environments. Payment Tokenization helps secure host-to-host connections and can therefore be applied across a wide range of use cases, including: For SAVYINT and Kryptus, Tokenization is not treated as an isolated security layer, but as part of a broader architecture encompassing HSM, Key Protection, Digital Identity, Authentication and Transaction Security. This combination is designed to protect not only payment data, but also the chain of trust underpinning every electronic transaction. Payment HSM – The Foundation for Cryptographic Key Protection Cryptographic keys are among the most critical assets within payment infrastructure. From encryption and authentication to payment information protection and cryptographic operations, the management and protection of keys have a direct impact on the security of the overall system. This is why Payment HSM plays a foundational role in a Secure Payment Infrastructure architecture. With its capabilities in HSM and cryptographic security, Kryptus provides a layer of protection for cryptographic keys and cryptographic operations in high-security environments. When combined with SAVYINT’s capabilities in PKI, Digital Signing, Authentication and Digital Identity, HSM becomes a foundational component of a Digital Payment Trust architecture — spanning from key protection to authentication and transaction security. From Identity Authentication to Transaction Protection A secure transaction must begin with accurately establishing identity and properly authenticating the party initiating the transaction. Strong authentication technologies, MFA and FIDO2/Passkeys help strengthen account protection and reduce reliance on traditional authentication methods that may be vulnerable to exploitation. However, user authentication is only one part of the equation. For high-value transactions, systems must also be able to verify the transaction itself that the user is authorizing. This is where Transaction Signing plays a critical role. Transaction Signing establishes a binding between an authenticated identity and the specific content of a transaction, enhancing protection against scenarios in which transaction details are altered or manipulated during processing. When Digital Identity, FIDO2/MFA and transaction signing are combined with HSM and Key Protection, the system can establish an end-to-end protection chain spanning the user, the transaction and the cryptographic assets supporting the transaction. Secure API and Open Banking – Protecting the Connected Ecosystem Open Banking is driving deeper connectivity among banks, Fintechs, Digital Wallets and third parties through APIs. This model creates significant opportunities for financial service innovation, while simultaneously expanding the attack surface and security requirements across the entire transaction flow. API Security must therefore be treated as an integral component of Secure Payment Infrastructure. A transaction flow needs to be protected end-to-end, from Identity and Authentication through API and Transaction Signing to Tokenization, transaction processing and Audit. Within this architecture, the combination of SAVYINT’s capabilities in Digital Identity, Authentication, Digital Signing and Transaction Security with Kryptus’s HSM and Key Security capabilities can create a unified layer of protection for Open Banking, Banking-as-a-Service, Digital Wallet and Fintech ecosystems. Preparing for the Future with Crypto Agility and PQC Next-generation payment infrastructure must not only address current security requirements but also be capable of adapting to changes in cryptographic technologies. The development of Post-Quantum Cryptography (PQC) is introducing new requirements for financial institutions and payment infrastructure providers. Systems need to be designed with the ability to transition between cryptographic algorithms and mechanisms when required, rather than being tightly dependent on a single technology. This is the foundation of Crypto Agility. An adaptable architecture needs to consider the ability to: Integrating HSM, Key Management, Digital Identity and Secure Transaction Architecture from the design stage provides a strong foundation for future Crypto Agility and PQC readiness, particularly when the architecture is built by a provider with deep integration capabilities across the latest quantum-resistant technologies, such as SAVYINT. From traditional banking to Digital Wallets, Fintech and Open Banking, payment infrastructure is becoming increasingly connected, distributed and complex. This also represents a natural expansion of Digital Trust. The collaboration between Kryptus and SAVYINT will bring a comprehensive solution ecosystem capable of addressing increasingly complex customer requirements, while supporting strict compliance with international standards for payment security, information security, digital identity and electronic authentication. Contact us
SAVYINT and Kryptus Partner to Build Sovereign Digital Trust Architecture for National-Scale Digital Identity
As countries accelerate the development of digital identity infrastructure and trusted digital services, the challenge is no longer limited to identity verification. It also requires building a Digital Trust foundation capable of protecting cryptographic keys, maintaining a robust Trust Hierarchy, ensuring transaction integrity, and meeting requirements for technological sovereignty. SAVYINT and Kryptus are working closely together across HSM systems, PKI infrastructure, digital signing, timestamping, electronic identity, mobile identity, and FIDO2/Passkey technologies, laying the foundation for Sovereign Digital Trust architectures designed for governments and public-sector organizations. This is not simply a combination of an HSM solution and a PKI platform. SAVYINT and Kryptus are pursuing a broader vision of connecting Cryptographic Trust with Identity Trust – from the protection of cryptographic keys to identity, authentication, and electronic transactions. From Cryptographic Trust to Digital Identity Trust A large-scale Digital Identity ecosystem requires multiple layers of trust to operate in coordination. At the foundational layer, HSMs and the Root of Trust play a critical role in protecting sensitive cryptographic keys and establishing the foundation for PKI. On top of this foundation, components such as Trust Hierarchy, Certificate Policy/Certification Practice Statement (CP/CPS), Key Ceremony, TSA/Timestamping, and Digital Signing help establish and maintain a trusted chain across the entire system. At the identity layer, Digital Identity, Mobile Identity, and FIDO2 extend the capabilities for authenticating and protecting user identities across digital environments. It is the integration of these layers that creates a Digital Trust architecture capable of meeting requirements at scale. And this is precisely where SAVYINT and Kryptus can complement each other. Kryptus – HSM and Root of Trust Foundation Kryptus brings deep expertise in cryptographic security and HSM technologies, providing a foundation for protecting critical cryptographic keys in high-security environments. Within a PKI architecture, an HSM is more than simply a security device. It can serve as a Root of Trust, protecting critical CA keys and supporting the establishment of a secure Trust Hierarchy. Kryptus also brings technological experience within the ICP-Brasil ecosystem, including environments associated with Root CA and Brazil’s public digital certification infrastructure. In addition to HSM technologies, Kryptus develops technologies related to timestamping and time-source management, further extending the role of cryptographic infrastructure in Digital Trust services. These capabilities form the Cryptographic Trust layer of the architecture envisioned by SAVYINT and Kryptus. SAVYINT – PKI, Trust Services and Digital Identity Building on the Root of Trust, SAVYINT contributes an ecosystem of Digital Trust and Digital Identity solutions, including TrustCA Remote Signing, TrustCA Timestamp, Passkey/FIDO2, and Mobile Identity. These capabilities extend from key protection and Trust Hierarchy establishment to services that directly support users and electronic transactions. Combined with Kryptus’s HSM and Root of Trust foundation, these capabilities create an end-to-end value chain spanning cryptographic foundation, trust services, digital identity, authentication, and digital transactions. SAVYINT × Kryptus: Combining Capabilities to Build Sovereign Digital Trust For governments and public-sector organizations, Digital Trust is increasingly linked to requirements for Sovereign Cryptography and Local Key Ownership. A Sovereign Digital Trust architecture should enable organizations to maintain control over critical cryptographic assets and key components of their trust infrastructure, including: With this approach, organizations can build Digital Trust infrastructure aligned with domestic legal and governance requirements while maintaining interoperability with international standards and ecosystems, including: Expanding further, countries can establish National PKI and National Digital Identity ecosystems, strengthening national sovereignty in cyberspace and enabling a more proactive and sustainable approach to digital trust. Contact us today to connect with leading experts in Digital Trust and Digital Identity! KRYPTUS SAVYINT Securing the Root. Empowering Digital Identity. Building Sovereign Digital Trust.
Global Financial Fraud in Recent Years: Alarming Figures

Financial fraud targeting financial activities is becoming increasingly complex and sophisticated. The use of artificial intelligence (AI) by criminals, together with the widespread standardization and replication of malware and other technologies, is acting as a major driver of fraudulent activities. Financial Fraud Is Increasing Globally In INTERPOL’s March 2026 Global Financial Fraud Threat Assessment, financial fraud ranks among the top five global crime threats, with a 54% rise in fraud-related Notices and Diffusions from 2024 to 2025. Global fraud losses climb to $442 billion. The number of INTERPOL Notices and Diffusions related to fraud increased by 54% between 2024 and 2025. The sharp increase in INTERPOL alerts reflects the growing complexity and scale of cross-border fraud. Payment fraud is increasingly taking place across multiple jurisdictions, making purely domestic control measures no longer sufficient. Payment card fraud losses worldwide dipped 1.2% to $33.41 billion in 2024, according to the Nilson Report, the leading trade publication covering the global payment card industry. This fraud was tied to global card volume of $51.920 trillion. The 2026 AFP Payments Fraud and Control Survey Report provides that payments fraud remains widespread, with 76% of organizations reporting that they experienced attempted or actual fraud in 2025. Checks remain the payment method most frequently impacted by fraud. In 2025, 58% of organizations reported check fraud, outpacing ACH fraud and wire fraud. Despite long-standing awareness of check-related risks, checks continue to present persistent vulnerabilities for many organizations managing payments fraud risk. Business Email Compromise (BEC) remains one of the most common forms of payment fraud, as criminals increasingly exploit impersonation techniques to manipulate organizational processes. A 2025 study by global technology research and consulting firm Juniper Research found that e-commerce fraud is expected to increase from $56 billion in 2025 to $131 billion by 2030, representing a 133% increase over the period. This growth is driven by the rising incidence of friendly fraud, in which legitimate transactions are fraudulently disputed. Key Financial Fraud Trends AI-powered deception AI-powered manipulation is rapidly changing people’s perception of what can be considered trustworthy. Advanced AI tools can generate “deepfakes” — including realistic voices, synthetic videos, and highly personalized text — making it easier to stage scenarios that appear completely authentic, even to generations highly familiar with digital environments. As technology advances and the digital world becomes increasingly visual, victims find it more difficult to question what they see or hear. The boundary between reality and fabrication is becoming increasingly blurred. This creates an increasingly complex and unpredictable fraud landscape. According to Koren, once again, understanding human behavior has become critically important. Fraud Is Becoming More Personalized and Persistent Between 2024 and 2025, the number of fraud incidents involving social engineering increased by 33%. This method is not only growing in scale but is also undergoing a fundamental shift in its approach. To address future forms of fraud, technological expertise alone is no longer sufficient; understanding human behavior is equally essential. One clear trend is that social engineering is no longer simply a technical attack, but has evolved into a prolonged process of influencing individuals. Whereas fraud previously often consisted of a single message, we are now seeing multi-step schemes in which trust is gradually built over days or even weeks. Criminals are increasingly using psychological tactics: they spend time learning about their victims, mimicking their language and behavior, and then gradually influencing them to make decisions that ultimately harm themselves. The Professionalization of Fraud Tools One clear emerging trend is the professionalization of fraudulent online storefronts. Scam websites have evolved significantly: they are no longer crude and poorly designed sites, but professionally built platforms with convincing e-commerce interfaces and close integration with digital marketing channels such as Facebook. Fraudsters can quickly create new stores with a trustworthy appearance within just a few hours, while flexibly adapting their visuals and messaging with remarkable sophistication. One alarming trend that Recorded Future called out is the increasing industrialization of support services and technology that allows fraudsters to maximize their effectiveness. One such popular tool allows scam operators to rewrite the code on an online retailer’s payments page and then steal, or “skim,” payment information as transactions happen in attacks called Magecart. The report points out that there were 10,500 such hacks active in 2025, leading to the compromise of over 23 million online transactions. These highly professional fraudulent commercial environments play a critical role in the constantly evolving fraud economy, targeting online shoppers through highly convincing storefront interfaces. Cross-Border and Distributed Fraud Operations We are also seeing a significant increase in cross-border fraud activities, particularly in the movement of illicit funds. Transactions are distributed across multiple countries, with participants — including both willing participants and individuals who are manipulated or unaware of the scheme — being used to break transaction flows into smaller segments, making them more difficult to trace. The recruitment of “money mules” often relies on psychological tactics involving financial pressure, social influence, and emotional manipulation. The “fraud economy” is becoming increasingly professionalized and global, while also becoming far more adaptable and resilient. Savyint Fraud Detection and Prevention Solutions With more than 20 years of experience in cybersecurity, information security, and cyber safety, particularly in the financial and banking sectors, Savyint has developed a comprehensive ecosystem of solutions for fraud detection, payment security, identity, authentication, and system access control. We leverage AI, AI agents, and the latest security standards to detect and respond to fraud, ensuring that every transaction conducted in our customers’ digital environments is protected in real time and capable of withstanding evolving and increasingly sophisticated forms of fraud over the long term. Our solution ecosystem includes: Contact us today for expert consultation HERE! Reference: https://www.helpnetsecurity.com/2026/03/18/online-fraud-victims-losses-interpol-report https://www.tietoevry.com/en/blog/2026/04/five-payment-fraud-trends-to-monitor https://www.mastercard.com/global/en/news-and-trends/stories/2026/recorded-future-annual-payment-fraud-report.html https://www.financialprofessionals.org/training-resources/resources/survey-research-economic-data/details/payments-fraud The Nilson Report
Singapore’s Singpass Introduces Passkeys to Strengthen National Digital Identity
The Government Technology Agency of Singapore (GovTech Singapore) announced the rollout passkey on Jun 30, 2026 as a new login method for Singpass, Singapore’s national digital identity platform. Singpass is every Singapore resident’s trusted digital identity to prove who we are when performing everyday transactions like checking our CPF balance, booking medical appointments, renewing insurance and more. Access over 2,700 services across 800 government agencies and businesses, simply by authenticating with your biometrics or SMS Two-Factor Authentication (2FA). Created by GovTech as a key enabler of Singapore’s digital economy, Singpass facilitates over 41 million transactions every month. Out of 5 million Singpass users, more than 4.2 million people use the Singpass app to easily log in to services, prove their identity over counters, digitally sign documents and do more on the go. Passkeys add to existing authentication methods such as QR login, Face Verification, and SMS One-Time Passwords (OTPs). Passkeys are a secure, password-free way to log in to services with Singpass. They are phishing resistant and use device-based authentication such as facial recognition, fingerprint, or app passcode to verify your identity. If a device is lost or stolen, the Singpass app and passkey on it will be automatically deactivated when the user sets up Singpass on another device. What is a Passkey? A passkey is a cryptographic key designed to replace passwords. As old passwords could easily be stolen, hacked, or even guessed, passkeys would work on a completely different level, with public-private key pairs authentication. Unlike a password, passkeys cannot be shared, remembered, or written down. This makes it far less vulnerable to the types of attacks that commonly target password-based systems. While early biometric authentication technologies laid the foundation for identity verification, the journey toward passkeys began in 2012 with the establishment of the FIDO Alliance, with the mission of eliminating passwords. The passkey revolution began in 2021, when major technology companies adopted the FIDO2 and WebAuthn standards, enabling passwordless authentication. Today, passkeys have become an authentication method accessible to billions of users worldwide. A significant milestone in the evolution of passkeys was the National Institute of Standards and Technology (NIST) formally recognizing synced passkeys in its supplement to the SP 800-63B guidelines. NIST SP 800-63B Supplement This recognition highlights the phishing-resistant nature of passkeys, while demonstrating their potential to replace traditional passwords with a more secure, convenient, and user-friendly authentication method. With NIST’s recognition, passkeys are well positioned for widespread adoption, particularly in highly regulated industries such as banking and healthcare. This is expected to drive the next phase of secure digital identity verification. The Difference Between Passkeys and Passwords Types of Passkeys There are two main types of passkeys, designed for different use cases and, more importantly, different security requirements. Within the digital security ecosystem, the two primary categories are Multi-Device Passkeys and Device-Bound Passkeys. Let’s explore the differences between them. Multi-Device Passkeys Multi-Device Passkeys, also known as Synced Passkeys, are well suited for personal use. They can be seamlessly synchronized across multiple devices, such as smartphones, tablets, and laptops, provided those devices are linked to an Apple, Google, or Microsoft account. This flexibility allows users to access their accounts from any trusted device without having to remember or enter a password. Device-Bound Passkeys In contrast, Device-Bound Passkeys can be viewed as a “security shield” for enterprise environments. Because they are bound to a single device and cannot be copied, this type of passkey provides an additional layer of security that is particularly valuable for organizations with strict data protection and access control requirements. In other words, Multi-Device Passkeys prioritize convenience and flexibility, while Device-Bound Passkeys prioritize stronger control and security. Benefits of Passkeys Benefits for Users Benefits for Developers As these technologies continue to evolve, more people are asking: What is a passkey, and how does it work? Growing interest in passkeys is encouraging technology innovators to invest significant resources in researching, developing, and advancing this technology. Passkeys are set to bring profound changes to security and digital identity while shaping how future generations interact with the digital world. Reference source: https://www.passkeys.com/ Contact us HERE to explore Savyint’s most advanced and secure solutions for authentication and digital identity.
eIDAS 2.0 – Reshaping a Safer and More Trusted Digital Future for Europe
Building on the foundation of eIDAS – the European framework for “Electronic Identification, Authentication and Trust Services” in the European Single Market – eIDAS 2.0 was introduced to strengthen the region’s digital infrastructure, promising greater efficiency and higher levels of trust in the digital economy. eIDAS – The Regulation on Electronic Identification, Authentication and Trust Services Approved in September 2014, the Regulation on “Electronic Identification, Authentication and Trust Services” for the European Single Market, known as eIDAS, became fully applicable in September 2018. Under eIDAS, European citizens and businesses can use nationally issued electronic identification systems to verify their identities when accessing public services or carrying out cross-border electronic transactions. eIDAS focuses on two key areas: Importantly, eIDAS applies not only to public authorities but also to private-sector organizations that use electronic identification or trust services, including those in the financial services, insurance, healthcare, and e-commerce sectors. As such, eIDAS serves as a unified digital trust infrastructure for cross-border electronic transactions across Europe. Why is eIDAS 2.0 Needed? Although eIDAS significantly improved Europe’s electronic identification and trust services infrastructure, several limitations remained. The emergence of new electronic identification services and models has resulted in a fragmented market. The scope of the existing legal framework no longer fully reflects the way electronic identification and trust services are being used in practice. Today, private companies also provide eID solutions, but these solutions do not necessarily follow a unified standard offering the same high levels of security, assurance, and transparency as eID schemes recognized under eIDAS. While eIDAS-compliant eID solutions are secure, their adoption and usability in the private sector have remained relatively limited. Challenges also exist in areas such as identity verification, data management, and user control. Today’s users expect a seamless and secure online experience. They want to access both public and private services such as healthcare and banking through a single, convenient digital identity or Single Sign-On (SSO) experience. However, the original eIDAS framework focused primarily on cross-border access to public services, while giving less attention to the needs of the private sector. Even for public services, barriers remain that prevent many citizens from accessing trusted electronic identification solutions. Social media platforms and private technology companies already offer login options based on existing accounts, such as Facebook, Microsoft, or Google. However, these solutions raise concerns regarding data control and security. They often lack robust real-world identity verification processes, potentially making systems more vulnerable. In addition, using these platforms across multiple services may result in non-transparent data sharing and privacy concerns. What is eIDAS 2.0? eIDAS 2.0 – officially known as the European Digital Identity Framework under Regulation (EU) 2024/1183 – is the updated version of the European Union’s framework for electronic identification, authentication, and trust services. The updated framework is designed to improve the efficiency of cross-border services while supporting secure electronic identification solutions for both the public and private sectors. eIDAS 2.0 represents a structural evolution of Europe’s digital identity and trust services framework. It addresses limitations in the original framework, expands the range of regulated trust services, strengthens security and governance requirements, and, most notably, introduces the European Digital Identity Wallet (EUDI Wallet) as a core component of Member States’ digital identity ecosystems. Key Changes Introduced by eIDAS 2.0 The transition from eIDAS to eIDAS 2.0 introduces two major developments aimed at strengthening Europe’s legal and regulatory framework for electronic identification and trust services. Expanded Trust Services eIDAS 2.0 further develops the regulatory framework for Qualified Trust Service Providers (QTSPs), with particular emphasis on identity verification processes for individuals and legal entities when qualified certificates are issued. The objective is to ensure greater consistency and harmonization across Europe. In addition, new qualified trust services – including electronic archiving, electronic ledgers, and the management of remote electronic signature devices – have been introduced under eIDAS 2.0. European Digital Identity Wallet (EUDI Wallet) One of the most significant innovations introduced by eIDAS 2.0 is the European Digital Identity Wallet (EUDI Wallet). The EUDI Wallet is a secure, user-controlled digital wallet that enables individuals to store, manage, and selectively share their identity data, credentials, and other personal information, as well as verified legal documents such as driving licences, educational qualifications, professional certificates, or bank account information. The Wallet can be used for both online and offline services, allowing users to conveniently share verified credentials with relying parties including government authorities and private-sector organizations for purposes such as identity verification or electronic signing. Under the original eIDAS framework, EU Member States had the discretion to decide whether to develop or notify official national electronic identification schemes. This resulted in significant differences in adoption rates among Member States and inconsistencies in cross-border interoperability. eIDAS 2.0 replaces this approach with a more unified and mandatory framework. By the end of 2026, each EU Member State is required to make at least one European Digital Identity Wallet (EUDI Wallet) available to its citizens and residents. Conclusion The adoption of eIDAS 2.0 marks a significant step toward a secure, interoperable, and trusted ecosystem for electronic identification and trust services across the European Union. By emphasizing user-friendly experiences, strong security mechanisms, and streamlined processes, eIDAS 2.0 is expected to deliver tangible benefits for citizens, businesses, and government institutions alike. While the detailed implementation roadmap is still being developed, the foundations have now been established for a safer, more inclusive, and more trusted digital future for people across Europe.
SAVYINT: Making Its Mark in the Australian Market
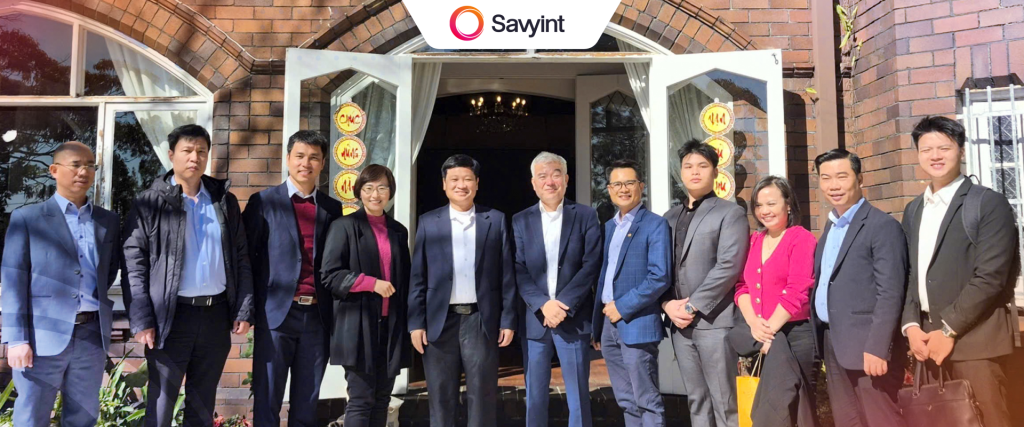
Recently, General Secretary and President Tô Lâm, together with a high-level Vietnamese delegation, paid a State visit to Australia, opening a new chapter for intellectual, technological and innovation cooperation between the two countries. On this occasion, Savyint was honored to join the delegation of the Ministry of Science and Technology in promoting technology and trade cooperation between Vietnam and Australia. Over the course of three working days, the Department of Digital Technology and Artificial Intelligence under the Ministry of Science and Technology organized a series of trade and investment promotion activities with the participation of representatives from Vietnam’s leading technology companies. During the program, Savyint engaged in open and in-depth discussions with leading Australian companies in AI and unmanned systems, as well as prominent universities specializing in science and innovation. These engagements included meetings with the Consulate General of Vietnam in Sydney; DroneShield, a leading defense technology company specializing in UAV detection and counter-drone solutions and a technology partner to the U.S. Department of Defense, NATO, and defense organizations across the Five Eyes alliance; Professor Wenjie Zhang of the University of New South Wales (UNSW) and N2N AI to explore research, technology transfer and commercialization opportunities in trusted and sovereign AI, semiconductors and autonomous drone technologies. The delegation also visited the UTS Tech Lab and met with Professor Diep Nguyen, Head of the UTS 5G/6G Laboratory, Director of the Adaptive Communications and Computing Group, and Director of Transnational Education at the Faculty of Engineering and Information Technology, University of Technology Sydney (UTS). Notably, at the Vietnam – Australia Digital Technology Experts and Businesses Networking Conference, Savyint had the opportunity to introduce its capabilities and connect with more than 30 technology companies and professionals, as well as Vietnamese and Australian experts and intellectuals through the Vietnamese Australian Scholars and Experts Association. The event marked another important step in Savyint’s journey toward the Australia – New Zealand market and its broader strategy of expanding its global network and international presence. SAVYINT is a technology company with extensive market experience and strong capabilities across Financial Services and Banking, Fintech, Healthcare, Education and Digital Government, supported by core expertise in cybersecurity, cryptography, digital identity, electronic authentication, electronic certification and trust services. Building on hands-on implementation experience and a broad technology ecosystem, the company focuses on developing specialized solutions for critical digital systems and infrastructure. Its key technology areas include Crypto & Security, Zero Trust, and fraud detection and prevention for AIoT devices, drones, Smart City systems, aerospace applications, and other environments with stringent requirements for cybersecurity and data protection. In the field of semiconductors and hardware security, SAVYINT is focused on developing technologies such as cryptographic chips, Security ICs, dedicated security chips, Hardware Security Modules (HSMs), and AI Security solutions, strengthening the protection of data, devices and systems from the hardware layer upward. These capabilities also provide the foundation for developing highly specialized and deeply integrated security products across multiple industries. Another key long-term strategic focus is Quantum Security and Quantum-Safe technologies. SAVYINT and SAVIS are investing in research and development of Post-Quantum Cryptography (PQC) and quantum-era cryptographic key management solutions, helping organizations proactively transition and strengthen their resilience against future threats posed by quantum computing. The company’s solutions are designed to comply with leading international security and payment standards, including eIDAS, PSD2/PSD3, NIST, FIPS, Common Criteria (CC), FIDO and PCI DSS. From a market perspective, the company is accelerating its business development and partnerships across Australia and New Zealand, with operations in Melbourne and Sydney, while also pursuing growth opportunities in ASEAN, ASEAN+2, the Middle East and India through its ecosystem of partners, investments and technology collaborations. The company’s goal is to progressively bring SAVYINT’s core technologies and advanced security solutions to regional and international markets. Highlights from the visit:
UAE’s Payment Authentication Revolution: The End of SMS OTP
On July 25, 2025, the Central Bank of the UAE (CBUAE) issued a landmark directive mandating all UAE banks to phase out SMS and email OTPs by March 2026. This pivotal move signals a major overhaul of the payment infrastructure, aiming to standardize in-app biometric authentication across the entire banking ecosystem. For years, SMS and email OTPs have been the go-to method for authenticating financial transactions. However, this approach has increasingly revealed vulnerabilities, including OTP leaks and delays due to inconsistent telecommunications infrastructure. Globally, fraud related to SMS OTPs caused a staggering $6.7 billion in losses in 2021. In the UAE alone, scams surged by 43% year-on-year, impacting over 40,000 individuals in 2023, making SMS OTPs an easy target for cybercriminals. To mitigate risks and enhance the user experience in payments and transactions, the CBUAE has directed the banking sector to adopt safer and more advanced authentication mechanisms integrated into mobile banking applications. The directive mandates all UAE banks to: This means that within the first eight months of implementation, financial institutions must develop a transition roadmap, test, and roll out new authentication systems to fully replace traditional OTPs. Users will no longer receive OTPs via SMS or email; instead, they will approve transactions directly within banking apps using fingerprints, facial recognition, or push notifications. This shift reduces transaction latency, enhances user experience, and strengthens security. Currently, banks like Emirates NBD and ADIB have already adopted biometric login and soft tokens, while many others still rely on traditional OTPs and must urgently upgrade before the deadline. This bold move by the UAE is expected to ripple across the GCC, particularly Saudi Arabia, within the next 12 months. A unified standard for secure payment authentication across the MENA region is likely to emerge, fundamentally transforming the current payment infrastructure. Savyint – Pioneering Strong Authentication Solutions for MENA Payments Amid increasingly stringent payment security and user authentication requirements, particularly with the CBUAE’s new regulations, SAVYINT – a global technology leader in open banking, data security, and authentication solutions – is poised to partner with financial institutions and payment service providers across the MENA region. SAVYINT delivers a comprehensive ecosystem of advanced strong authentication solutions, fully compliant with international standards and leveraging cutting-edge passwordless technologies to elevate user experience: SAVYINT offers a robust suite of authentication solutions for payments and transactions: By combining robust authentication technologies with strict adherence to international security standards such as FIDO2, PSD2, eIDAS, GDPR, and PCI DSS, Savyint’s solutions enable banks, fintechs, and service providers in MENA to rapidly deploy modern, flexible authentication platforms that integrate seamlessly with existing systems and fully comply with CBUAE regulations. Connect with Savyint’s experts today to build a secure and compliant payment ecosystem.
Establishing Digital Trust in Banking
As digital services continue to grow, user expectations for security and data privacy are rising. Digital Trust has become a competitive advantage in banking, where financial institutions must not only deliver services but also demonstrate reliability in protecting customers’ personal data, assets and privacy. What is Digital Trust? Digital Trust is the confidence customers place in an organization’s ability to protect data, ensure secure transactions, and comply with regulations. It extends beyond mere trust in a business to include confidence in technology, data management, operational transparency, customer service, and adherence to fair, lawful practices. For example, Public Key Infrastructure (PKI) provides a foundation for secure digital identity, document signing, data encryption, and timestamping—core elements for a secure and reliable digital experience. Broadly, adopting PKI is part of building Digital Trust, reinforcing customer confidence in an organization’s ability to safeguard data, comply with laws, and operate transparently. The Importance of Digital Trust in Banking Digital Trust is critical for financial institutions, as banks handle vast amounts of sensitive information daily, from personal data and transaction histories to financial assets. Strengthening Digital Trust enables organizations to: The Core Pillars of Digital Trust in Banking To build robust Digital Trust, banks must focus on six key pillars: security, transparency, privacy, data integrity, ethical technology use, and regulatory compliance. Each pillar plays a critical role: Protecting customer data from unauthorized access, cyberattacks, and fraud is paramount. Banks should adopt modern security technologies, such as: + Data encryption + Multi-factor authentication (MFA) + Biometric authentication (fingerprint, facial recognition) Privacy goes hand-in-hand with security. Banks must minimize unnecessary data collection and sharing while empowering users with transparent, understandable privacy policies and control over their data. Customers must know how their data is used, who has access, and what safeguards are in place. Transparency—from clear privacy policies to timely communication of changes—builds trust. In case of breaches, banks should have response mechanisms in place, including timely customer notification, damage control, and fair compensation if needed. User-friendly and secure authentication is essential for trusted digital transactions. Banks should implement solutions such as: + Biometric authentication + Blockchain-based identity management + Strong authentication to prevent unauthorized access A secure digital identity process also helps banks comply with KYC requirements while ensuring customer convenience and data protection. Customers expect up-to-date, accurate data—from account balances to transaction records. Banks should ensure this by: + Conducting regular audits + Establishing clear data verification processes + Maintaining transparent reporting systems Artificial Intelligence (AI) and Machine Learning (ML) can further enhance reliability by detecting anomalies, automating data handling, and ensuring data consistency. As AI becomes more integrated into banking—from loan suggestions to credit scoring—banks must ensure: + AI systems provide fair, unbiased recommendations, without discrimination based on gender, age, geography, or income (e.g., not denying loans solely based on rural residence). + Use of Explainable AI, allowing customers to understand decisions made. + Clear feedback and appeal channels if customers disagree with AI-driven decisions. To establish Digital Trust, organizations must adopt technology platforms recognized for compliance with national and international standards, ensuring secure, transparent, and verifiable digital transactions. For example, PKI enables secure encryption, digital signing, and identity verification. Leveraging services from trusted providers and adhering to standards like eIDAS, FIPS, GDPR, and ISO/IEC 27001 demonstrates a serious commitment to protecting customer data and privacy. Digital Trust is now a strategic priority in the digital transformation of financial institutions. Building it through robust security, transparency, privacy, data integrity, and ethical technology use is essential for banks to maintain a leading position. Establishing Digital Trust with SAVYINT SAVYINT is a global technology company pioneering open banking, data security, and protection across critical sectors like Finance-Banking, Government, Manufacturing, Telecommunications, Healthcare, Education, and Media. Beyond being a trusted service provider, SAVYINT offers electronic authentication services, including timestamping and Qualified Trust Services (QTSP) for digital signing and electronic seals through its QTSP Remote Signing solution. With extensive experience in designing, deploying, and operating electronic identity systems (eKYC), digital signing, data encryption, and PKI and CA systems (national, internal and public CAs) for numerous banks and financial institutions, SAVYINT provides a comprehensive suite of solutions to establish Digital Trust: Connect with SAVYINT experts HERE to establish Digital Trust for your organization!
eKYC solution using HyperLedger Fabric
The Central Bank of Bahrain (“CBB”) has has launched the eKYC by financial institutions in the Kingdom as part of its initiatives for digital transformation in the sector. The eKYC solution built by Bahrain BENEFIT utilizes hyperledger Fabric Blockchain platform. The platform was built in collaboration with Avanza Innovation company. The national eKYC platform, which was the first of its kind in the region targeting retail banks, financial services providers and money exchange networks, is operated by BENEFIT in collaboration with the Information and eGovernment Authority (IGA) and under the supervision of the CBB. The platform provides a national digital identity database for financial institutions to securely verify the identities of their customers, validate their information and share data digitally before providing products and services. This includes retrieval of customer data from governmental entities including IGA. BENEFIT has also developed the Application Programming Interface (“API”) for the platform, which allows for seamless integration with financial institutions core systems, digital channels and mobile apps. With the introduction of Open Banking in Bahrain, this also provides an opportunity for fintech companies to verify customers identities through their online and mobile applications. Mr. Khalid Al Hamad, Executive Director of Banking Supervision at the CBB said “The CBB urges all licensed financial institutions to avail of this innovative and streamlined service and accelerate its efforts towards automating the maintenance of its customer data and reputation records, by implementing eKYC API integration with their core systems, digital channels and mobile apps. We continue to support technological advancement in the sector to minimize cost while also fostering innovation and integration between financial institutions and fintech companies. This is also in line with the CBB’s continuous efforts in developing the financial sector infrastructure in light of the Covid-19 repercussions to ensure appropriate solutions for electronic payment systems.” BENEFIT’s Chief Executive Officer Abdulwahid Janahi said “It gives us great pleasure to continue developing the eKYC platform in an effort to drive digital transformation in the Kingdom’s various sectors. We have succeeded in enabling the integration of this digital platform into core banking systems and smart phone applications, and we are pleased to announce that Bahrain Islamic Bank has successfully integrated this platform into its core banking services system, while “ila” Bank offers customer on-boarding in a completely digital and autonomous manner through its mobile app, both based on eKYC API integration. We look forward to the use of eKYC services on a larger scale during the coming period.” The Vice Chairman of eTransformation in the Information & eGovernment Authority (iGA), Dr.Zakareya Ahmed Alkhaja, confirmed that iGA cooperated with “BENEFIT” that implemented the technical development of the project, under the supervision of CBB. The project aims to provide an advanced comprehensive eSystem for financial entities to verify the identity of their customers and the validity of the information, before providing the financial services. He pointed out that the authority has started providing identity verification services to the government sector, and this project complements providing the services to the private sectors, especially the banking sector, as the project will allow the it to start providing innovative, high-quality, secure data services that keep the privacy of individuals. That will lead to enhance economic growth and expand commercial activities in the Kingdom. He expressed his pride that the (eKYC) project is the first of its kind in the region and the first at the level of global applications in terms of cooperation between the government and the banking sector, as the implementation of projects globally is limited to cooperation between banks in the private sector. This project is also one of the first Projects using Block Chain technology in the Kingdom of Bahrain. Source: https://www.unlock-bc.com/news/2021-02-01/central-bank-of-bahrain-launches-hyperledger-fabric-ekyc-platform-with-benefit/