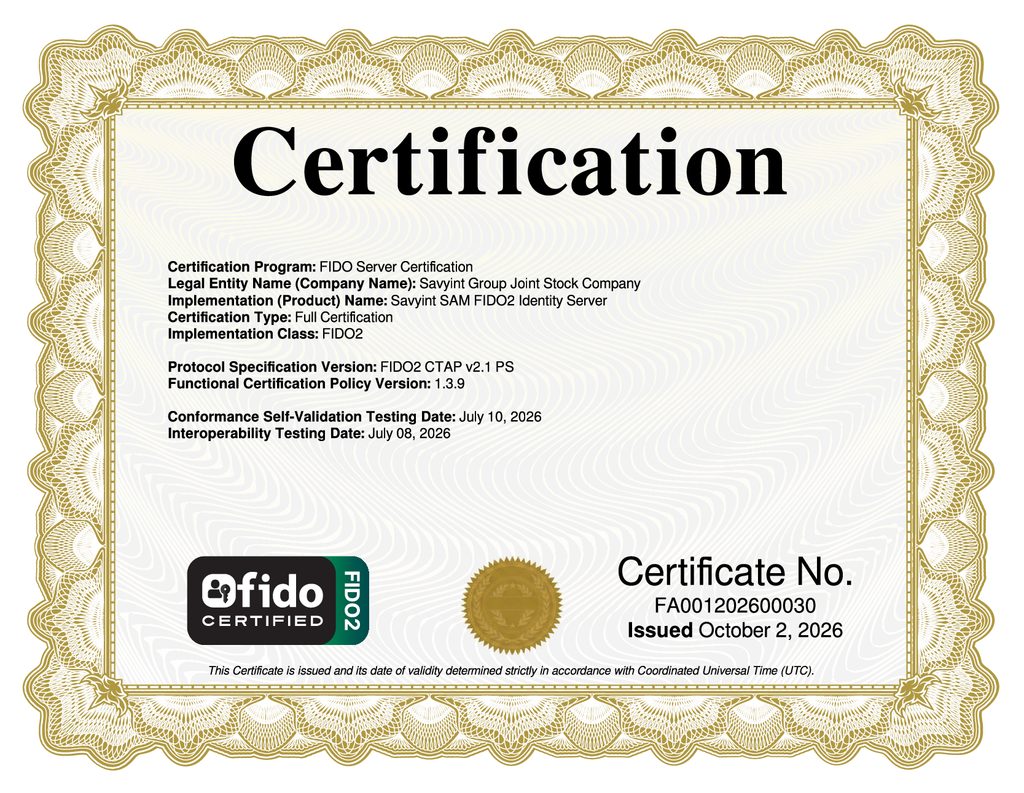
On October 2, 2026, SAM FIDO2 Identity Server, developed by Savyint Group Joint Stock Company, officially achieved Full Certification under the FIDO Server Certification program. This milestone recognizes SAVYINT’s capabilities in developing authentication solutions aligned with international standards, with technical conformance and interoperability verified.
Officially Certified Under the FIDO Server Certification Program
Following testing, evaluation, and the completion of the required documentation in accordance with the FIDO Alliance’s certification process, SAM FIDO2 Identity Server was awarded FIDO Server Certification – FIDO2 CTAP v2.1 PS. To achieve certification, the product underwent two key testing activities, including technical conformance testing and interoperability testing with other components in the FIDO2 ecosystem.
Technical Conformance Testing – Conformance Self-Validation is the process of verifying whether a product’s implementation meets the applicable technical requirements. This process uses FIDO testing tools to assess conformance with the relevant criteria.
Interoperability Testing assesses the server’s ability to operate and interact with other authentication components within the FIDO2 ecosystem. Test scenarios include key processes such as user registration and authentication, thereby verifying the product’s interoperability.
FIDO2 – A Foundation for Modern Authentication in Digital Services
As organizations and businesses increasingly deliver services through digital channels, identity authentication and access control have become essential to protecting accounts, data, and transactions.
FIDO2 is a set of authentication standards based on public-key cryptography that supports modern authentication methods, including passwordless authentication. This technology helps reduce reliance on traditional passwords and strengthens defenses against phishing and credential theft.
Within the FIDO2 ecosystem, the authentication server plays a critical role in managing registration and authentication processes and interacting with related components. Technical conformance and interoperability are therefore essential to ensuring that authentication operates in accordance with the intended technical design.
Advancing SAVYINT’s Technology Capabilities and Digital Trust Vision
The Full Certification of SAM FIDO2 Identity Server marks an important step forward in SAVYINT’s development of secure authentication technologies. This achievement recognizes the product’s conformance and interoperability within the scope of the FIDO certification program, while reflecting SAVYINT’s commitment to developing solutions based on international technical standards.
With a strategic focus on developing the Digital Trust ecosystem, SAVYINT continues to invest in identity authentication, access security, and technologies that enhance the security of digital services. These capabilities provide a foundation for businesses and organizations to progressively strengthen security, deliver convenient authentication experiences, improve customer experiences, and meet security requirements throughout their digital transformation journeys.
About SAM FIDO2 Identity Server
SAM FIDO2 Identity Server is a passwordless mobile identity and authentication solution developed based on FIDO2 standards, combining data encryption and transaction security. The solution addresses requirements related to blockchain, cryptocurrencies, mobile payments, data encryption, transaction encryption, system security, and authentication, complying with the security requirements of modern digital ecosystems.
SAM FIDO2 Identity Server comprises:
- Hardware Security Module (HSM), ensuring security in accordance with FIPS 140-3 Level 3 or Common Criteria EAL4+ (EN 419 221-5), with a crypto-agile architecture and post-quantum cryptography integration.
- FIDO2 Server software and digital signing software, including remote digital signing, HSM-based signing, Signing Server, USB digital signatures, and token/smartcard-based signing.
SAM FIDO2 Identity Server is built on a Zero Trust security architecture and integrates modern technologies, including:
- FIDO2/WebAuthn Level 3
- Support for CTAP 2.1 and CTAP 2.3 authentication
- Full lifecycle management of Passkeys
- Device Trust and device authentication
- Risk-based adaptive authentication
- Transaction authorization and authentication
- Identity federation through OIDC/OAuth 2.0/SAML
- Hardware-backed encryption using HSM technology
- Pioneering adoption of NIST post-quantum cryptography (PQC) standards
- Cryptographic agility
Leveraging public-key cryptography, SAM FIDO2 Identity Server eliminates risks associated with traditional password exposure, phishing, credential theft, and other digital fraud threats. At the same time, the solution ensures strict compliance with international standards and the regulations of individual countries:
- Vietnam: Circular No. 50/2024/TT-NHNN, Circular No. 64/2024/TT-NHNN, Circular No. 77/2025/TT-NHNN, the Law on Personal Data Protection, the Law on Cybersecurity, and other applicable regulations.
- Philippines: The Anti-Financial Account Scamming Act (AFASA), BSP Circulars Nos. 1213, 1214, and 1215.
- Malaysia: Risk Management in Technology (RMiT) policy, the Personal Data Protection Act (PDPA), and other applicable regulations.
- GCC/MENA: Personal Data Protection Laws (PDPL), Bahrain’s Open Banking regulations, and other applicable requirements.
Contact the SAVYINT team for consultation [HERE].