

From Open Banking to Open Finance and Open Data
The Open Banking ecosystem is expanding rapidly, bringing significant and positive changes to the global financial landscape. The world is now ready to witness the next chapters in the evolution of Open Finance and Open Data. In fact, Open Banking emerged somewhat unexpectedly. In the UK, as Fintech companies began entering the retail payments market, there were initially no specific regulations governing how these parties should collaborate or operate within the ecosystem. A study conducted by the UK Competition and Markets Authority (CMA) found that the UK retail banking sector was highly concentrated, with limited competition. These findings provided a major impetus for the introduction of Open Banking regulations and similar initiatives worldwide, aimed at enhancing competition and driving economic growth. This led to the emergence of Open Banking, with its principles and requirements formally established under the European Parliament’s PSD2 Directive and, more recently, the proposed PSD3 framework. Key roles were also clearly defined, including Account Information Service Providers (AISPs), which aggregate users’ financial data from multiple accounts, and Payment Initiation Service Providers (PISPs), which enable payment services across accounts. The emergence of Open Banking has encouraged banks to invest in API technology and establish partnerships with Fintech organizations across Europe. Nordic banks were among the earliest and most enthusiastic adopters of this model. Digital Identity as an Enabler of Open Finance and Open Data The Nordic countries provide a compelling example of how digital identity can be adopted in banking for commercial purposes. As digital identity solutions become widely used across the region, they help accelerate customer authentication and streamline digital financial services. This has enabled Fintech companies not only to compete with traditional banks, but also to challenge credit and debit card providers, whose services have traditionally faced limitations in online customer information management. Beyond authentication, digital identity provides a trusted foundation for Open Finance and Open Data. By enabling secure identification, reliable authentication and consent-based data sharing, digital identity solutions can help users access financial services across multiple providers while maintaining control over their personal information. Integrated with secure APIs and consent management platforms, digital identity can support trusted data exchange among banks, Fintech companies and other authorized third parties, paving the way for more connected, interoperable and user-centric financial ecosystems. Open Data Enables Competition and Drives Innovation Following its implementation and widespread adoption, Open Banking has developed more rapidly than initially anticipated. Today, users can authorize banks to share their transaction histories, identification images and other relevant information with other banks or third-party providers of their choice. They can also switch accounts, apply for loans or obtain credit cards from new providers with greater ease. In addition, users can manage their financial histories through a single platform, eliminating the need to switch between multiple applications. This transformation is gaining momentum as new players enter the ecosystem. In the future, organizations outside the financial sector will also leverage Open Data to deliver highly personalized products and services, while allowing users to retain control over their own data. These new market participants will make it easier for users to discover and access services that meet their specific needs. Ultimately, services that significantly reduce time and costs will be well positioned to attract and retain users. Open Data – An Opportunity for Early Movers From the perspectives of regulators and users alike, the transition to Open Banking and Open Finance is not something that can be achieved overnight. It requires a continuous, long-term process. Greater attention will also be needed as new technological initiatives around Open Data emerge. For Open Data to drive meaningful and positive change, clear regulatory frameworks and legal standards are essential. This requires concerted efforts from regulatory authorities, as well as closer international cooperation to establish common standards and requirements for secure, compliant data exchange across borders. In conclusion, the world is witnessing the continued growth of Open Banking and the benefits it brings. It is now time to set the next goals for the era of Open Finance and Open Data. While this transformation will take time, it will serve as a powerful catalyst for global economic and technological development. SAVYINT – Comprehensive Open Banking Solutions SAVYINT provides a comprehensive Open Banking solution ecosystem, encompassing data management, Digital Identity and trusted digital services. Backed by more than 20 years of experience in the Banking and Financial Services sector, SAVYINT has successfully deployed solutions for leading banks and major organizations across Vietnam and Southeast Asia (SEA). The solution portfolio includes: Contact us today to consult with our leading Open Banking experts HERE!
SAVYINT and Kryptus Advance Secure Payments with Digital Identity, Tokenization and HSM Technology
As digital payments, Open Banking and Digital Wallets continue to evolve rapidly, payment security is no longer limited to protecting card data. Financial institutions need a comprehensive security architecture that provides end-to-end protection – from user identity, authentication and transactions to cryptographic keys, payment data and API connectivity. SAVYINT and Kryptus are working together to combine complementary capabilities in Payment HSM, Payment Tokenization, Digital Identity, Strong Authentication, Transaction Signing and Secure API, with the goal of building a Secure Payment Infrastructure for banks, digital wallets, Fintechs and digital payment ecosystems. Under the partnership framework, Payment Tokenization has been identified as one of the key use cases, alongside Government Digital Identity & Digital Signing. This approach is designed to extend cryptographic protection and Digital Trust capabilities from the infrastructure layer to high-value digital financial transactions that require robust security, control and scalability. Comprehensive Security Across the Entire Transaction Lifecycle A digital payment transaction today can involve multiple components, including user identity, authentication mechanisms, banking or digital wallet applications, APIs, payment processing systems, card data, cryptographic keys and third-party services. As ecosystems become increasingly interconnected, a vulnerability at any layer can potentially affect the security of the entire transaction. Payment security therefore needs to be designed as an end-to-end chain of trust, rather than focusing solely on individual components. In the architecture envisioned by SAVYINT and Kryptus, the protection chain consists of: Digital Identity, Strong Authentication, Transaction Signing, Tokenization, HSM & Key Protection, Secure API, Audit & Compliance. This approach connects Identity Trust with Cryptographic Trust and Payment Trust, creating the foundation for a secure and scalable digital payment architecture. Payment Tokenization – A Key Focus of the Partnership The growth of Apple Pay, Android Wallet, Digital Wallets, mobile payments and card-on-file services is transforming the way users store and make payments. In this model, Payment Tokenization plays an important role in reducing direct exposure to sensitive payment data. Instead of using original payment data throughout transaction flows, tokens can be used in appropriate, controlled contexts and environments. Payment Tokenization helps secure host-to-host connections and can therefore be applied across a wide range of use cases, including: For SAVYINT and Kryptus, Tokenization is not treated as an isolated security layer, but as part of a broader architecture encompassing HSM, Key Protection, Digital Identity, Authentication and Transaction Security. This combination is designed to protect not only payment data, but also the chain of trust underpinning every electronic transaction. Payment HSM – The Foundation for Cryptographic Key Protection Cryptographic keys are among the most critical assets within payment infrastructure. From encryption and authentication to payment information protection and cryptographic operations, the management and protection of keys have a direct impact on the security of the overall system. This is why Payment HSM plays a foundational role in a Secure Payment Infrastructure architecture. With its capabilities in HSM and cryptographic security, Kryptus provides a layer of protection for cryptographic keys and cryptographic operations in high-security environments. When combined with SAVYINT’s capabilities in PKI, Digital Signing, Authentication and Digital Identity, HSM becomes a foundational component of a Digital Payment Trust architecture — spanning from key protection to authentication and transaction security. From Identity Authentication to Transaction Protection A secure transaction must begin with accurately establishing identity and properly authenticating the party initiating the transaction. Strong authentication technologies, MFA and FIDO2/Passkeys help strengthen account protection and reduce reliance on traditional authentication methods that may be vulnerable to exploitation. However, user authentication is only one part of the equation. For high-value transactions, systems must also be able to verify the transaction itself that the user is authorizing. This is where Transaction Signing plays a critical role. Transaction Signing establishes a binding between an authenticated identity and the specific content of a transaction, enhancing protection against scenarios in which transaction details are altered or manipulated during processing. When Digital Identity, FIDO2/MFA and transaction signing are combined with HSM and Key Protection, the system can establish an end-to-end protection chain spanning the user, the transaction and the cryptographic assets supporting the transaction. Secure API and Open Banking – Protecting the Connected Ecosystem Open Banking is driving deeper connectivity among banks, Fintechs, Digital Wallets and third parties through APIs. This model creates significant opportunities for financial service innovation, while simultaneously expanding the attack surface and security requirements across the entire transaction flow. API Security must therefore be treated as an integral component of Secure Payment Infrastructure. A transaction flow needs to be protected end-to-end, from Identity and Authentication through API and Transaction Signing to Tokenization, transaction processing and Audit. Within this architecture, the combination of SAVYINT’s capabilities in Digital Identity, Authentication, Digital Signing and Transaction Security with Kryptus’s HSM and Key Security capabilities can create a unified layer of protection for Open Banking, Banking-as-a-Service, Digital Wallet and Fintech ecosystems. Preparing for the Future with Crypto Agility and PQC Next-generation payment infrastructure must not only address current security requirements but also be capable of adapting to changes in cryptographic technologies. The development of Post-Quantum Cryptography (PQC) is introducing new requirements for financial institutions and payment infrastructure providers. Systems need to be designed with the ability to transition between cryptographic algorithms and mechanisms when required, rather than being tightly dependent on a single technology. This is the foundation of Crypto Agility. An adaptable architecture needs to consider the ability to: Integrating HSM, Key Management, Digital Identity and Secure Transaction Architecture from the design stage provides a strong foundation for future Crypto Agility and PQC readiness, particularly when the architecture is built by a provider with deep integration capabilities across the latest quantum-resistant technologies, such as SAVYINT. From traditional banking to Digital Wallets, Fintech and Open Banking, payment infrastructure is becoming increasingly connected, distributed and complex. This also represents a natural expansion of Digital Trust. The collaboration between Kryptus and SAVYINT will bring a comprehensive solution ecosystem capable of addressing increasingly complex customer requirements, while supporting strict compliance with international standards for payment security, information security, digital identity and electronic authentication. Contact us
From Open Banking to Banking-as-a-Service: What Comes Next?
Over the past decade, financial innovation has evolved from open banking, which focuses on consumer-authorized data sharing, to banking-as-a-service (BaaS), which uses application programming interfaces (APIs) to make core banking functions more modular and accessible. Open banking & Open Finance The term “Open Banking” emerged around 2016 as a policy initiative aimed at increasing competition in the retail payments sector. The United Kingdom was the first country to explore this approach as a regulatory tool for promoting greater competition in digital payments through the Open Banking Implementation Entity. The idea behind these initiatives was straightforward: by making it easier for third-party providers (TPPs) to access data, regulators could lower barriers to entry, encourage competition, and create more opportunities for innovation in digital payments. A similar approach was taken by the European Union through the Second Payment Services Directive (PSD2), which came into effect in 2018. PSD2 required banks to provide registered third-party providers with access to customer account data through standardized application programming interfaces (APIs). Open Finance takes this concept a step further. While Open Banking mainly focuses on banking and payment data, Open Finance covers a much broader range of financial products and services, including credit, investments, pensions, and insurance. Under an Open Finance model, consumers can give third parties access to a broader set of financial data, potentially providing a more complete picture of their financial lives. While the potential benefits of Open Finance have not yet been fully demonstrated in practice and evidence of its impact remains limited, the concept could give consumers and businesses greater control over their financial data. By making more financial data available, Open Finance could help reduce information gaps, encourage competition, and create opportunities for more personalized financial products. These products could better reflect an individual’s financial profile, spending habits, and long-term goals. Open Finance can also make it easier for consumers to bring together and compare information from multiple providers, helping reduce complexity and make financial decisions easier. Concept of Everything-as-a-Service (XaaS) Against this backdrop, Open Banking is often seen as one of the starting points for the rise of Banking-as-a-Service (BaaS) – a new approach to financial services that brings data-driven capabilities into the way banking services are delivered. BaaS is built around the broader concept of Everything-as-a-Service (XaaS), also known as Anything-as-a-Service. XaaS refers to a wide range of cloud-based and remotely delivered services that companies can access through the Web or similar networks. The idea started with Software-as-a-Service (SaaS), where cloud providers made individual software applications available to customers. Over time, the model expanded into other services such as Infrastructure-as-a-Service (IaaS) and Communications-as-a-Service (CaaS). Eventually, the concept developed into the broader XaaS model, where businesses can access the specific services they need and pay for them on demand. In simple terms, instead of buying a software license and installing the application on individual computers, a business can subscribe to a cloud-hosted application provided by the software company. This approach gives businesses greater flexibility to switch providers while also making software maintenance easier. APIs play a key role in making this possible. They allow different applications and software systems to communicate and work with each other. As XaaS continues to grow, opportunities are also expanding for developers to build third-party applications that connect with existing platforms. The growth of SaaS, for example, has created entire businesses around developers and companies using SaaS platforms. However, APIs and SaaS are not the same thing. APIs do not require SaaS, and they have existed long before the Internet. They can also be used in offline environments. LinkedIn is an example of the SaaS model because it delivers its platform through cloud computing and generates revenue through recurring subscription fees. Facebook, on the other hand, does not operate as a SaaS company. Although it provides data through APIs, its primary source of revenue is advertising, much like Google’s core business model. Unlike SaaS providers, these platforms do not rely on subscription fees for their core services. Bank as a Service What banks can now build with APIs follows a similar XaaS approach. Banking-as-a-Service enables banks to deliver digital banking capabilities through APIs. In other words, banking services can move beyond traditional branches and become part of mobile and web-based experiences. Banks can make their data, functions, and infrastructure available through APIs, allowing other digital platforms and businesses to integrate banking capabilities into their own services. From the customer’s perspective, this can lead to very different types of digital experiences. A bank may continue to interact directly with customers, or it may operate behind the scenes as a white-label service provider. In either case, customers no longer have to interact with their bank in the traditional way. Instead, APIs allow consumers to interact with companies that may not be banks themselves, while still being seamlessly connected to regulated financial institutions through digital interfaces. While Open Banking has opened the door to greater data sharing, its role as a data-sharing mechanism can still have limitations. BaaS, meanwhile, can act as a catalyst for creating more seamless and integrated financial services in the digital economy. This model allows banks to move toward more customer-centric, platform-based business models. For traditional banks, this may also mean rethinking and restructuring how they operate. In many ways, the future of financial institutions could increasingly resemble the broader XaaS model. Making this transition possible requires a connected and collaborative ecosystem, where integration is at the core and APIs become a key enabler. Savyint provides a comprehensive Open Banking and BaaS ecosystem, backed by more than 20 years of experience in the Banking and Financial Services sector, with successful deployments for leading banks and major organizations across Vietnam and Southeast Asia (SEA). Contact us to start your banking digital transformation journey today HERE! Source: From open banking to banking-as-a-service – Nydia Remolin
Open Banking: APIs, Data, and User Consent
Open Banking is the development of a new financial ecosystem based on connections between financial institutions and businesses, supported by APIs. Financial institutions are enabling third parties to integrate services, provide access to banking data, and deliver entire banking services through APIs. So how can APIs, data, and user consent be managed and protected? Key Characteristics of Open Banking Open Banking focuses on serving consumers, with API or SDK technology as its core foundation and operates within the financial ecosystem. Open Banking has three key characteristics: data portability, customer autonomy, and recipient accountability. The International Organization for Standardization (ISO) defines data portability as “the ability to easily transfer data from one system to another without having to re-enter the data.” Based on this definition, in Open Banking, consumers can share their relevant banking data with third-party providers (TPPs), in line with “data portability.” Data portability in Open Banking is supported by standardized and interoperable data technologies, primarily APIs. This is a fundamental principle of liberal democracy, in which marketers are permitted to influence customers but must respect their autonomy. Open Banking empowers customers to control the sharing of their banking data, and this right is supported by customers’ legal rights to share data through Open Banking. Open Banking requires recipients of customers’ banking data (TPPs) to be accountable to customers. Therefore, Fintech companies receiving banking data must be responsible for protecting this data from leakage, theft,… This is why strict management of TPPs through a regulatory system is very important. In summary, these three characteristics of Open Banking all reflect the goal of improving competitiveness, promoting innovation, and strengthening consumer protection. Solutions for Managing APIs, Data, and User Consent With many years of experience in developing security solutions as well as specialized solutions for the Financial – Banking sector, Savyint has developed an Open Banking Tech Stack solution that enables banks to comply with the current legal regulations of each country (such as EU PSD2/3, Philippines AFASA, BSP Circular No. 1213 – 1215, Vietnam Circular No. 64, Circular No. 50, Circular No. 77…), ensuring end-to-end security across API protection, payment, data sharing, and consent management operations. In particular, the solution is flexibly designed by Savyint according to scale, prioritizing the use of existing security infrastructure: small banks can deploy it in a simple and lightweight manner; large banks can scale up to a highly redundant model, ensuring continuous and stable operations even in the event of incidents. Contact us now for consultation HERE!
SAVYINT Develops Open Banking Tech Stack – Enabling Secure, Flexible, and Compliant Open Banking Connectivity
Savyint Open Banking Tech Stack enables banks to build and operate an Open Banking ecosystem on a unified architecture, covering TPP management, API management and delivery, consent management, data sharing, and payment initiation. Open Banking is becoming a key pillar of digital transformation strategies across Vietnam’s banking and financial services sector. Through open API, banks can connect with Third-Party Provider (TPP), FinTech, and digital platforms to provide services such as account information access, financial data sharing, and payment initiation. In this context, API serves as the key bridge connecting banks with the broader ecosystem. However, API connectivity also means that banks must extend their security controls beyond internal systems to encompass multiple partners, applications, and users. Every API transaction must be authenticated, access-controlled, and protected to ensure data integrity. At the same time, regulations governing open API deployment, cybersecurity, data protection, and related requirements have been introduced across many countries, including Singapore and Vietnam (Circular No. 64, Circular No. 50, Circular No. 77…), as well as the Philippines (AFASA and BSP Circular Nos. 1213–1215) … Compliance with these requirements has become a critical priority for banks. Banks must not only secure APIs but also protect cryptographic key, authentication information, signature, and evidence associated with data exchange and transaction processing. They must also maintain activity logs, detect anomalous access, and ensure that all operations are traceable for auditing purposes. Therefore, one of the key challenges facing banks today is how to leverage existing infrastructure while integrating the missing capabilities into a unified, comprehensive, scalable Open Banking architecture that can strictly comply with applicable regulations. SAVYINT’s Implementation Solution With extensive expertise in Open Banking, Open Finance, and payment security, Savyint provides a comprehensive HSM-powered Open Banking Tech Stack that enables banks to comply with applicable regulations while strengthening security across API protection, payment processing, data sharing and consent management. SAVYINT’s Open Banking Tech Stack is designed on a Microservices architecture, allowing banks to deploy capabilities in phases, leverage existing systems, and easily expand their Open Banking services in the future. With Savyint Open Banking Tech Stack, banks can build a centralized Open Banking ecosystem where data, consent, and transactions are managed end-to-end on a unified platform. This enables seamless connectivity with FinTech, ecosystem expansion, and the development of new digital financial services, while supporting full compliance with applicable regulations across markets governing open API, data security, and payment transactions.
Common Challenges in Consent Management
Customer data is a valuable asset for organizations and businesses. Without a structured, transparent system, companies may face numerous challenges, or even risk compromising customer trust. Typical Challenges in User Consent Management Most businesses and organizations understand the importance of consent management. However, in practice, the majority still manage it manually, in a fragmented way, with limited oversight. Common challenges in managing user consent management include: Incomplete or invalid consent collection Many organizations collect consent through default checkbox plugins, registration forms, often accompanied by terms of service that span dozens of pages and combine multiple purposes. Unintentionally, these practices can violate fundamental data protection laws, as they may not rely on voluntary consent and often fail to provide full, specific, clear, and detailed information to users. Fragmented consent management Organizations interact with customers through multiple touchpoints: mobile apps, internet banking, service counters, emails, SMS, and more. Each channel often has its own mechanism for collecting consent, which can lead to: These inefficiencies affect user experience and complicate organizational data management. Non-compliance with legal regulations Data protection laws are constantly evolving. What is valid today may no longer be valid tomorrow. Different regions and countries have different requirements. Violating international regulations can result in fines up to €20 million or 4% of annual global revenue under GDPR (EU), or USD 7,500 under CCPA (US). In Vietnam, banks must comply with the Personal Data Protection Law 2025 and Decree 356/2025/ND-CP. User personal data must be collected, stored, processed, and shared transparently, with mechanisms ensuring user rights to access, edit, revoke consent, and delete data when no longer necessary. Ensuring ongoing compliance with both international and local regulations is a significant challenge for organizations. Modern Consent Management Architecture Today, a modern consent management system is more than just a pop-up or a checkbox form. It is a complex technical system with multiple layers, ensuring that consent is collected accurately, stored securely, and remains consistent across the organization’s digital ecosystem. A modern consent management system typically includes the following pillars: About Savyint Consent Management SAVYINT is a global technology company with extensive experience in building secure digital infrastructure and digital trust for financial institutions, governments, and large enterprises. Built on an API-first and Zero Trust architecture, Savyint Consent Management automates the entire consent management process – from collection and storage to verification and revocation – ensuring transparency and control over user data. Integrating advanced technologies such as AI/ML and Post-Quantum Cryptography (PQC), Savyint Consent Management leverages immutable logs and homomorphic encryption to maximize security for sensitive data, enabling organizations to: Savyint Consent Management meets international standards such as GDPR, PDPA, CCPA, ISO 27701, PCI DSS, and local regulatory requirements in countries including Vietnam (Personal Data Protection Law 2025, Decree 356/2025/ND-CP, Circulars 64, 50, 77 from the State Bank of Vietnam), Singapore (PDPA), and more. Upgrade your consent management system and protect customer data today with Savyint, CONNECT NOW.
Savyint Trains Strategic Partner Vietnet: Leveling Up On Digital Trust, Open Banking & Next-gen Security
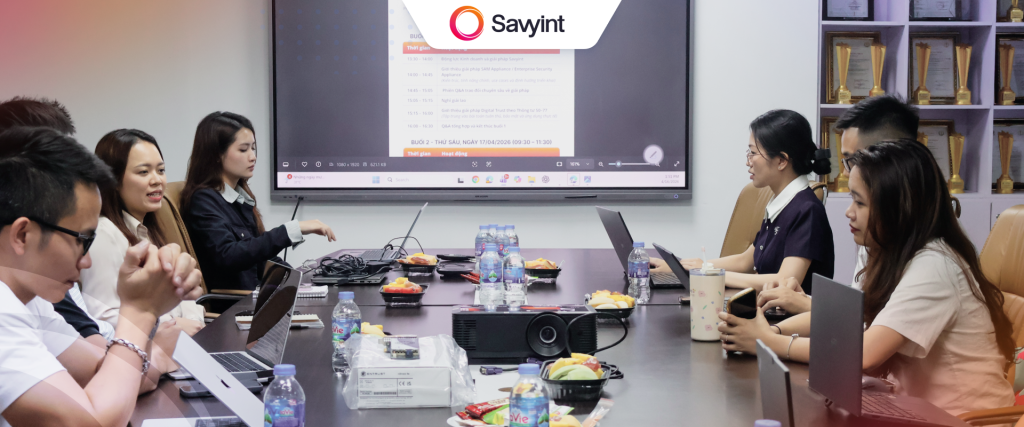
With data security, digital authentication, and legal compliance getting stricter by the day, Savyint recently held a training session for the strategic partner, Vietnet, to help Vietnet level up their consulting, deployment, and business development skills around next gen security, Digital Trust, and Open Banking – all fully aligned with Vietnam’s State Bank Circulars 50, 77, and 64. The program took place over two days (April 16–17, 2026) in Hanoi. It’s part of our long term strategic partnership to equip Vietnet with deep expertise and real world implementation skills – so they can bring world class security solutions to customers right here in Vietnam and across the ASEAN region. SAM Appliance – All in one data encryption, digital signature & mobile identity On the first training day, Savyint’s experts walked everyone through today’s biggest security challenges: the explosion of connected devices, tough compliance rules (GDPR, PCI DSS, eIDAS…), and the pressure to move toward post quantum cryptography (PQC). That’s where SAM Appliance comes in. It’s a complete package for data encryption, digital signatures, and mobile identity – fully compliant with standards for remote digital signatures, blockchain, cryptography, mobile payments, transaction encryption, time stamping, system security, IoT, Car2X, and more. But SAM Appliance isn’t just about signing invoices, contracts, certificates, or payment files. Built on a Cryptographic Security Platform (CSP), it also includes SCA & MFA, passwordless PKI based authentication, tokenization, end to end transaction signing, advanced mobile cryptography, and support for Post Quantum Cryptography (PQC) algorithms – ready for the next era of security. Plus, it integrates blockchain and cryptocurrency, enables mobile payments and digital wallets, and supports long term digital preservation with timestamps for 5, 10, even 20 years. SAM Appliance proudly meets regional technical standards and international regulations, including FIPS 140 2 Level 3, ISO 9001:2015, ISO 14001:2015, ISO 27001:2022, GDPR, SOC 2 Type II, HIPAA, and PCI DSS. Alongside all the technical details, the Vietnet team also got to explore real life use cases from banking, finance, and government – so they can see exactly how the solution fits each customer’s unique challenges. Digital Trust & Compliance Beyond SAM Appliance, Savyint offers a full Digital Trust solution stack designed to strictly follow local and international legal requirements. It’s built on four pillars: Risk Management & Compliance, Cyber Security & App Protection, SCA/MFA Identity, and FMS AI Fraud. On top of strong authentication (passwordless with FIDO2/Passkey, biometrics, contextual auth, Smart OTP, push notifications…), the solution adds AI and Machine Learning. This helps banks and financial institutions detect, assess, and stop fraud across the entire user journey – from login behavior and device fingerprints to access context and transaction details. Combine that with RASP+ (runtime app protection) and TrustShield – a mobile fraud prevention platform using device fingerprinting, behavior analysis, and AI – and you get a seriously robust defense. These pillars form a complete, end to end architecture that protects devices, behavior, identity, and transactions all at once. This is Savyint’s real strength: building high value, long term solutions that keep customers safe while staying compliant across multiple markets – like Vietnam (SBV Circulars 50, 64, 77), the Philippines (AFASA Act, Circulars 1213–1215), Malaysia (MRiT, PDPA), and beyond. Expanding capabilities with Open Banking Day two of the training focused on the Open Banking Tech Stack – fully compliant with Circular 64/2024/NHNN. It includes: • Savyint Open Banking Portal, Savyint API Management, Savyint Consent Management • Savyint CIAM/SCA (PSD2), eKYC • Savyint TPP Management, Fraud Prevention & Risk Management Savyint is positioned not just as a tech vendor, but as an end to end Digital Trust platform – providing the security and compliance layer for the entire Open Banking ecosystem. Sprinkled throughout the technical sessions were open Q&A discussions where Savis and Savyint could talk through real world scenarios, challenges, and implementation tips. This training is part of Savyint’s long term strategy to build a strong partner ecosystem in Southeast Asia – and to cement our position as a leader in Digital Trust, Open Banking, and next gen data security. Some snapshots from the training program:
Consent Management in Open Banking
Open Banking is a new financial ecosystem that allows users to securely share their personal financial data with third-party providers, such as fintech companies or other financial institutions. By sharing this data, these organizations can provide personalized financial services to users. So, how is Open Banking data processed, and for what purposes is it used? Open Banking: Consent Management To provide and develop high-quality products and services, Third-Party Providers (TPPs) require user consent to access their financial data. From there, they filter and process this data for research purposes and to build new financial products and services. Consent management is a sensitive matter that requires caution and expertise in both legal and technical aspects. Contrary to popular belief, consent management is not just a simple click or checking an “I Agree” box; it is a structured process implemented in compliance with regional and national regulations and directives, such as PSD2/PSD3 or GDPR in the EU. The consent management process in banking typically unfolds as follows: While different organizations may present data access agreements differently, this is the most common mechanism, often used in: Understanding how data and information flow during the consent request process is a decisive factor for transparency and the success of organizations in Open Banking. The Process of Managing Consent for Open Banking Data Sharing The consent management process is generally divided into three stages: a. Consent Stage b. Authentication Stage c. Authorization Stage Throughout every process, users always know who they are granting access to, for how long, and for what purpose. Most importantly, users can revoke consent at any time. The information available to users typically includes: Open Banking Data Sharing: How Does It Work? Open Banking allows third-party financial service providers to access information with user permission. Technically, this process is facilitated via Open APIs. Legally, the data-sharing process is overseen and governed by existing government regulations, such as the Payment Services Directive (PSD2) in the EU or the Open Banking Act in the UK. However, as these regulations vary by region, the types of data shared through open banking services also differ. Typically, to ensure transparency and integrity, there are multiple layers of security and verification during the data exchange between financial institutions and TPPs. Data transmission is executed in a “heartbeat” thanks to APIs, ensuring a seamless, secure, and efficient experience. Who Can Access Open Banking Data? Not everyone can access data in Open Banking. To view this data, user consent is mandatory, and the TPP must be licensed. TPPs must also meet specific requirements before being authorized to access a user’s financial information. Dedicated competent authorities are responsible for licensing TPPs to access user data. For example, in Australia, the Australian Competition and Consumer Commission (ACCC) is responsible for Open Banking data licensing. These agencies ensure that personal financial data sharing does not violate the law while having the power to grant, modify, or revoke data collection licenses. What Data is Collected in Open Banking? The data collected by open banking service providers may vary depending on the regulations of each country/region and the type of service provided. Regulators often set strict rules on the type of information that can be collected, limiting the scope to ensure TPPs only access what is strictly necessary. The most commonly collected data includes: How Does Open Banking Protect User Data? Protecting data in Open Banking is a top priority for regulators and financial institutions. Security measures applied include: However, alongside these protections, certain risks remain of concern to developers and users: In summary, while risks cannot be entirely eliminated, current security measures are established to ensure user data is protected within the open banking system. Nevertheless, users should also protect themselves by using strong passwords, updating software regularly, and staying vigilant against phishing attacks. Furthermore, empowering users to manage their open banking data is an excellent way for them to take responsibility for when and how they wish to provide their information. TPPs must clearly communicate the purpose and the data to be collected to ensure transparency and Open Banking data privacy. Savyint and Savyint Consent Management As an global technology company with extensive expertise in PKI, Cryptography, Blockchain, Electronic Identification, Authentication, Savyint proudly introduces Savyint Consent Management, specifically designed for the collection, storage, and transparency of user data rights. As an international technology group with extensive expertise in PKI, Cryptography, Blockchain, Electronic Identification, Authentication, and Open Banking/Finance, Functioning as a central “Trust Engine,” this solution automates 100% of the processes for collecting, storing, and verifying data rights across the entire customer journey. Savyint Consent Management enables enterprises to process sensitive data with total transparency, ensuring full compliance with global and local regulations such as Vietnam’s Personal Data Protection Law (No. 91/2025/QH15), Circular 64/2024/TT-NHNN, GDPR, FAPI 2.0… Advanced Technologies of Savyint Consent Management: Connect with Savyint’s experts today to lead the way in the data security era and build sustainable digital trust!
From AFASA to BSP Circulars 1213 – 1215: SAVYINT Partners with Philippine Banks to Strengthen Security and Fight Digital Fraud
The rapid growth of digital banking, e-wallets, and online payments in the Philippines has led to a serious consequence – financial fraud is becoming increasingly sophisticated and more organized. Following the enactment of AFASA, the Bangko Sentral ng Pilipinas (BSP) continued to issue BSP Circulars 1213, 1214, and 1215, tightening the responsibilities of financial institutions and imposing stricter requirements for user authentication, fraud management, and data protection. About AFASA and BSP Circulars 1213, 1214, and 1215 Officially taking effect on June 25, 2025, the Anti-Financial Account Scamming Act (Republic Act No. 12010) was enacted by the Philippine government with the following core objectives: One of the most important requirements under AFASA is the mandatory transition of authentication methods before June 2026. OTPs sent via SMS and email will no longer be accepted for high-risk transactions. Instead, more secure methods must be implemented, such as biometric authentication, passwordless authentication, and adaptive multi-factor authentication (MFA) based on risk levels. AFASA marks a major shift in risk management thinking: account security is no longer just a technology choice – it is now a legal obligation. BSP Circular 1213 – Focus on Fraud Management and Strong Authentication Among the three circulars, BSP Circular 1213 is considered the technical backbone that brings AFASA into real operational practice. This circular requires banks and financial institutions to: BSP Circular 1213 clearly states that traditional authentication methods are no longer sufficient. Systems must understand user behavior patterns and detect fraud at the earliest stages – during login or even before a transaction is completed. Read more: Philippines BSP Circular No. 1213 and Compliance Solutions for Financial Institutions BSP Circular 1214 – Enabling Data Sharing for Faster Fraud Response BSP Circular 1214 addresses a major legal bottleneck related to accessing account data during fraud investigations. Its main goal is to create a fast-response mechanism to prevent funds from being completely withdrawn before authorities can intervene. Under this regulation: BSP Circular 1215 – Protecting Funds During Disputes While Circular 1213 focuses on prevention and 1214 focuses on investigation, BSP Circular 1215 addresses what happens after an incident occurs. It allows financial institutions to protect customer funds during the investigation period, preventing money from “disappearing” within minutes. Specifically, this circular: Together, AFASA and BSP Circulars 1213, 1214, and 1215 are reshaping the digital financial security standards in the Philippines. Financial institutions now need not only compliance documentation but also a strong technology foundation capable of detecting, preventing, and responding to fraud in real time. AFASA & BSP 1213, 1214, 1215 – Compliant Security Solutions from SAVYINT Savyint is a leading trusted service provider, ready to deliver authentication and payment security solutions that strictly comply with security standards and regulatory requirements under AFASA, BSP Circulars 1213, 1214, and 1215 issued by the Bangko Sentral ng Pilipinas (BSP), as well as the Philippine Open Banking framework and international regulations. Savyint’s solution ecosystem is built around four key pillars: Risk Management & Compliance, Cybersecurity & Application Protection, SCA/MFA Identity, and the FMS AI Fraud Engine. Together, these components protect the entire customer journey – from registration, login, authentication, and transaction execution to post-transaction monitoring. SAM Auth Server SAM Auth Server is an all-in-one strong authentication solution designed for mobile payments and digital banking. Built on a Zero Trust architecture and integrated with a FIPS 140-3 Level 3 certified Hardware Security Module (HSM), and ready for Post-Quantum Cryptography, SAM Auth Server supports a wide range of modern authentication methods, including: Biometric authentication, Smart OTP, Push Authentication, FIDO2 / Passkeys and Context-based authentication It enables step-up authentication when risk levels increase, ensuring maximum protection for electronic transactions. SAM FIDO2 Identity Server SAM FIDO2 Identity Server is a passwordless identity and authentication platform based on FIDO2/WebAuthn standards. It eliminates password storage by replacing passwords with asymmetric key-based authentication securely stored on the user’s device.As a result, the system effectively protects against common attacks such as phishing, man-in-the-middle attacks, and credential stuffing. SAM FIDO2 Identity Server fully meets Strong Customer Authentication (SCA) requirements under PSD2/PSD3 and complies with international standards for identity and data security. SAVYINT Fraud Prevention & Risk Management SAVYINT Fraud Prevention & Risk Management leverages AI and Machine Learning (ML) to help banks and financial institutions detect, assess, and prevent fraud across the entire user journey – from login behavior, device characteristics, and access context to transaction data. Key capabilities include: RASP+ RASP+ protects mobile applications directly within the runtime environment, detecting and blocking attacks while the application is running. It can detect rooted or jailbroken devices, debugging attempts, code tampering, hooking techniques, memory manipulation and emulator-based attacks. RASP+ integrates directly into mobile applications without affecting performance, ensuring strong protection without compromising user experience. TrustShield TrustShield is a mobile fraud prevention platform powered by device fingerprinting, behavioral analytics, and AI. It can identify devices without relying on cookies or advertising IDs, detect emulators, rooted or jailbroken devices, identify multi-device fraud patterns, analyze in-app user behavior, generate real-time risk scores and trigger adaptive authentication directly on mobile devices. With a multi-layered architecture and seamless integration capabilities, Savyint’s security ecosystem delivers a comprehensive fraud prevention model – protecting devices, behavior, identity, and transactions simultaneously. All solutions comply with AFASA, BSP Circulars 1213, 1214, 1215, and international standards such as FIDO2, PSD2/PSD3, eIDAS, GDPR, and PCI DSS. This allows fast deployment on existing infrastructure while achieving the highest level of security. Connect with Savyint’s experts today to implement and optimize your security solutions – and be fully prepared to meet AFASA and BSP requirements within just 3 months!