

SAVYINT HEALTHCARE DAY 2026: MODE ON – CHECK UP
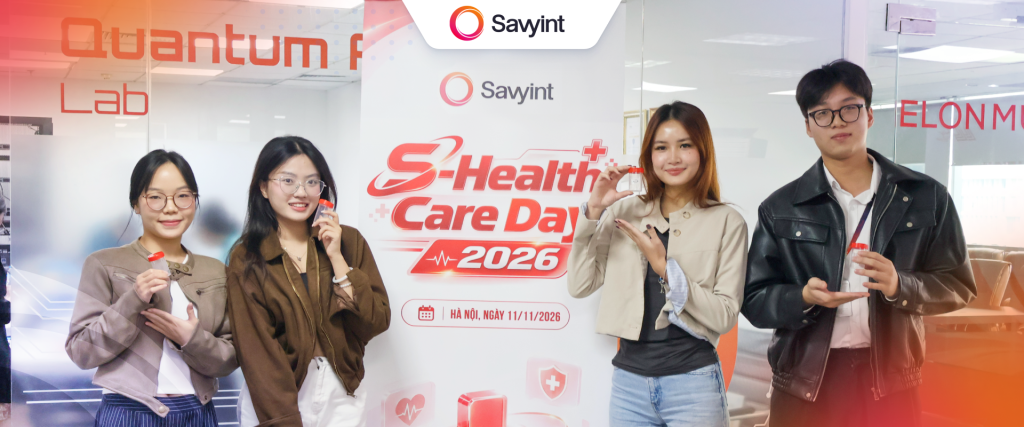
With the aim of fostering a healthy and sustainable working environment, Savyint Healthcare Day is an annual initiative that encourages every employee to prioritize personal health, proactively monitor their well-being, and develop positive, healthy lifestyle habits. Under the theme “Mode on – Check up,” Savyint Healthcare Day 2026 reinforces the importance of proactive healthcare and sustainable self-care practices. Following the format of previous years, the programme comprises two stages: an initial health screening at the Savyint office, followed by comprehensive examinations at a general medical clinic. On the morning of November 12, the clinic’s medical team arrived at the office lobby to collect blood and urine samples. Employees also provided their personal information and medical history, received guidance from healthcare professionals, and completed the procedures required for the first stage. The second stage takes place at the general medical clinic, where employees undergo a comprehensive range of examinations and assessments, including: Through a structured examination process and professional medical support, the programme helps employees better understand their health, identify potential concerns early and make informed decisions about their ongoing care. Savyint Healthcare Day 2026 reflects Savyint’s commitment to employee well-being and a corporate culture that places people at the centre of its development. By investing in employee health, Savyint strengthens the foundation for an engaged, resilient workforce equipped to achieve shared goals and contribute to sustainable business growth. Highlights from Savyint Healthcare Day 2026:
OpenID4VC HAIP: Enabling Secure and Interoperable Digital ID Wallets
The OpenID4VC High Assurance Interoperability Profile (HAIP) is a technical specification officially published by the OpenID Foundation in December 2025. It is playing a central role in shaping national and international digital identity wallet ecosystems. 1. What is the OpenID4VC High Assurance Interoperability Profile (HAIP)? The OpenID4VC High Assurance Interoperability Profile (HAIP) defines a set of requirements for existing standards to ensure interoperability among credential Issuers, Wallets, and Verifiers in scenarios requiring high levels of security and privacy. This technical specification aims to achieve high levels of security and privacy through the following characteristics: HAIP uses the “OpenID for Verifiable Credential Issuance” [OIDF.OID4VCI] and “OpenID for Verifiable Presentations” [OIDF.OID4VP] protocols as the foundation for credential issuance and presentation. The supported credential formats include: Both credential formats can be issued through a single interaction with the Authorization Server. High-Level Security (Security & FAPI Profile): Key Binding & Attestation: Supports Wallet Attestation and Key Attestation through KB-JWT to ensure that only the legitimate Holder can present credentials. 2. HAIP in the European Digital Identity Wallet (EUDI Wallet) HAIP (High Assurance Interoperability Profile) serves as the core set of rules for technical alignment within the European Digital Identity Wallet (EUDI Wallet) project. It helps ensure that digital wallets issued by any EU Member State can operate seamlessly and securely across all countries within the Union. The specific application of HAIP within the EUDI Wallet ecosystem includes the following aspects: a. Standardizing Credential Issuance and Presentation Processes The EUDI Wallet operates through two main actions: receiving official documents from the government (Issuance) and presenting documents when required (Presentation). HAIP establishes common protocols for these two processes: b. Supporting Both Mandatory EU Data Formats Europe requires EUDI Wallets to support both credential formats to accommodate different online and offline scenarios. HAIP seamlessly integrates both: c. Ensuring the Highest Level of Assurance under eIDAS 2 Under the EU’s amended eIDAS Regulation, EUDI Wallets must achieve the highest security level (Assurance Level: High). HAIP addresses this through stricter technical requirements: d. Applying Financial-Grade Security Standards (FAPI 2.0) To protect EU citizens’ personal data from cyberattacks, HAIP applies the FAPI 2.0 (Financial-grade API) security profile to the EUDI Wallet. HAIP is the architectural core that helps turn the European Union’s vision of a secure, protected, and borderless digital wallet into a technical reality. 3. SAVYINT Digital ID Wallet: Advancing Secure and Interoperable Digital Identity As the digital identity landscape moves towards greater interoperability and high-assurance standards, Digital ID Wallets are becoming a key component of trusted digital ecosystems. Building on the principles of secure credential issuance, storage, and presentation highlighted by OpenID4VC HAIP, SAVYINT’s Digital ID Wallet solution aims to empower individuals to securely manage and use their digital identities and credentials across digital services. With a focus on security, interoperability, and user-centric digital identity management, SAVYINT is committed to supporting organizations in developing trusted digital identity ecosystems and advancing the adoption of digital identity wallet solutions. Connect with SAVYINT to explore our Digital ID Wallet solution and discover new opportunities to build secure, interoperable, and trusted digital identity experiences. Source: https://openid.net/specs/openid4vc-high-assurance-interoperability-profile-1_0.html#section-1-3.1
SAVYINT Advances Mobile ID Wallet and Cross-Border Digital Trust Capabilities
SAVYINT Global is advancing its SAVYINT Mobile ID Wallet, powered by its core Digital Trust technologies and designed to enable citizens and businesses to verify their identities, receive, store and share digital credentials, and sign documents securely on their mobile devices. Built to support cross-border digital trust services, the platform is underpinned by TrustCA QTSP 2.0, with Tayllocox providing advisory, assessment and certification support for eIDAS 2.0 and NIS compliance. It aims to deliver the security and interoperability required by evolving international standards and the EU regulatory framework, including provisions taking effect from 1 January 2027. What sets the platform apart is three layers in a single app: citizen authentication through VNeID for every service offered in the wallet; a digital credential wallet built on the OpenID4VC High Assurance Interoperability Profile (HAIP), published by the OpenID Foundation in December 2025. As digital transformation accelerates, mobile-based digital identity and wallet solutions are becoming essential to providing secure, convenient, and seamless access to digital services. In response to this growing demand, SAVYINT is advancing its Mobile Identity & Digital Wallet platform, designed to bring digital identity, electronic credentials, and essential digital services together in a unified mobile experience. 1. SAVYINT Mobile ID Wallet: one platform, three layers of capability The platform provides every component a country, ministry or financial institution needs to run a complete digital credential ecosystem: 2. Full compatibility with international digital ID wallet standards SAVYINT Mobile ID Wallet is compatible with the following international standards, so credentials it issues or verifies work with other conformant wallets, issuers and verifiers, in Vietnam and abroad: Standard How the platform applies it OpenID4VCI Credential issuance into the wallet under OpenID for Verifiable Credential Issuance; presentation over OpenID4VP; aligned with the OpenID4VC HAIP profile ISO/IEC 18013-5 ISO mdoc format for mobile driving licences (mDL) and identity documents; in-person presentation over NFC, BLE and QR, even without a network SD-JWT VC IETF SD-JWT VC format for online transactions, with selective disclosure FAPI 2.0 Financial-grade security profile for every API between wallet, issuer and verifier; DPoP, PKCE S256 and ECDH-ES/A128GCM response encryption FIDO2 Passwordless authentication with device-bound passkeys (WebAuthn L3, CTAP 2.1) through SAM FIDO2 Identity Server CSC API v2.0 / v2.2 Cloud Signature Consortium remote-signing interface between the wallet and TrustCA QTSP eIDAS 2.0 Aligned with the EUDI Wallet architecture under Regulation (EU) 2024/1183; TrustCA QTSP certified by Tayllorcox (EU) under eIDAS 2.0 and NIS2 3. User experience: authenticate, store, share, sign The app is designed so that citizens can use it straight away without needing to understand the technology behind it. The journey has four steps: authenticate through VNeID, keep credentials in the wallet, share selectively when asked, and sign remotely with TrustCA. Sector Typical scenario Public services Authenticate through VNeID, file administrative procedures online without paper copies, and sign applications on the phone Digital banking Account opening, authentication of high-value transactions under Circulars 50/77, remote signing of loan agreements Credit information Consent-based sharing of credit data that the customer can revoke at any time Telecom Verified SIM registration, safe SIM replacement and protection against SIM-swap fraud Transport Show a digital driving licence to traffic police even offline; rail, metro and boarding passes Healthcare, education Hospital check-in with a digital health insurance card; instant verification of diplomas and certificates 4. Partnering with SAVIS to Advance the Super App Ecosystem SAVIS is a Vietnam-based technology company with extensive experience in developing and deploying digital trust, cybersecurity, and eGovernment solutions. Its capabilities span national-scale Public Key Infrastructure (PKI), mobile Digital Identity and Electronic ID (eID), Qualified Trust Services (QTSP), remote digital signatures, and Mobile PKI. SAVIS also provides advanced identity verification and authentication technologies, including FIDO2 and Passkey, biometric authentication, eKYC, and ID verification, alongside anti-fraud solutions such as SIM Swap detection and prevention. With a portfolio of products and solutions serving government agencies, financial institutions, and enterprises, SAVIS has also received international recognition, including the Asia-Pacific ICT Alliance (APICTA) Awards, ASOCIO Awards. Building on these capabilities, SAVYINT will work alongside SAVIS to integrate and deploy the Mobile Identity & Digital Wallet platform within the eGov Super App ecosystem. The collaboration aims to connect digital identity and wallet capabilities with VNeID and online public services, creating a unified mobile platform for citizens to access and use digital government services. Through this collaboration, SAVYINT and SAVIS seek to strengthen the digital identity infrastructure underpinning the eGov ecosystem, enabling secure identity verification, convenient access to digital documents, and seamless connections to public services. By combining SAVYINT’s expertise in Digital Identity, Authentication, and Digital Trust with SAVIS’s capabilities in eGovernment platforms and system integration, the two companies aim to advance a comprehensive Mobile Super App ecosystem, bringing identity, documents, and public services closer to citizens through a single digital experience. 5. Building the Future of Mobile Digital Identity With its SAVYINT Mobile ID Wallet, SAVYINT aims to contribute to the development of secure, interoperable, and user-centric digital identity ecosystems in Vietnam and internationally. Connect with SAVYINT to explore our SAVYINT Mobile ID Wallet solutions and discover opportunities to build integrated digital identity and service ecosystems.
OpenID Connect and OAuth 2.0: Authentication vs. Authorization
OpenID Connect & OAuth 2.0 are important authorization and authentication protocols for access management across websites and applications. So, what exactly are these two concepts? Let’s explore them in the article below. What is OpenID Connect? OpenID Connect (OIDC) is an identity authentication protocol built on top of OAuth 2.0. It verifies users’ identities and passes the verified identity information to applications in a standardized, token-based format. Introduced by the OpenID Foundation in 2014, OIDC is now one of the most widely adopted standards for modern identity federation and Single Sign-On (SSO). What is OAuth 2.0? Meanwhile, OAuth 2.0, short for “Open Authorization,” is a standard designed to allow a website or application to access resources hosted by other web applications on behalf of a user. It replaced OAuth 1.0 in 2012 and has since become the de facto industry standard for online authorization. OAuth 2.0 provides consent-based access and restricts the actions that a client application can perform on resources on behalf of a user, without requiring the user to share their login credentials. Principles of OAuth 2.0 OAuth 2.0 is an authorization protocol, NOT an authentication protocol. Therefore, it is designed as a means of granting access to a set of resources, such as remote APIs or user data. OAuth 2.0 uses Access Tokens. An Access Token is a piece of data representing permission to access resources on behalf of an end user. OAuth 2.0 does not define a specific format for Access Tokens. However, in some cases, the JSON Web Token (JWT) format is commonly used. This allows token issuers to include data directly within the token itself. However, it does not tell the application who the actual user behind the token is. Why Is OAuth 2.0 Alone Not Enough? This gap created a practical problem. As platforms such as Google, GitHub, and Facebook evolved into identity providers, each returned user profile data in a different format. Developers building applications that support multiple sign-in options had to write custom code to handle each provider. There was no common standard for the format of “user identity” in responses. OIDC was developed to address both issues simultaneously: adding authentication to OAuth 2.0 and standardizing how user identity data is structured and transmitted. Aspect OAuth 2.0 OpenID Connect (OIDC) Purpose Authorizes access to resources Authenticates the user’s identity Core Token Access Token ID Token (plus Access Token) Use Case “Can this app access my data?” “Who is the user logging in?” Focus Secure resource access Secure and verified user login Data Scope Permissions only Identity + Permissions How OIDC Authentication Works Explore Identity and Access Management Solutions with SAVYINT As digital services continue to evolve, secure authentication and authorization are essential to protecting user identities and managing access to digital resources. SAVYINT provides advanced digital identity and authentication solutions designed to help organizations strengthen security, streamline access management, and build trusted digital experiences. Visit SAVYINT to learn more about our solutions and connect with our experts to explore how we can support your organization’s identity and access management needs. Reference: https://www.oloid.com/blog/what-is-oidc-authentication https://www.loginradius.com/blog/identity/oidc-authentication-security
Passwordless Authentication: Addressing Vulnerabilities in Banking Authentication
Passwords have long been part of banks’ authentication processes, but their role has diminished significantly. Passwordless Authentication goes a step further by eliminating the use of shared secrets altogether and replacing them with credentials that are resistant to phishing and large-scale compromise attacks. Vulnerabilities Persist in Banking Authentication Account takeover fraud remains one of the most serious threats to digital banking. Although many banks no longer use passwords as a standalone authentication factor, current authentication and account recovery processes still rely on mechanisms that can be exploited through phishing, information interception, or social engineering. Recent industry analyses indicate that criminals are shifting towards identity-based attacks. According to TransUnion’s latest fraud trends report, account takeover and identity impersonation are accounting for an increasingly large share of fraudulent activities. In practice, attackers commonly use the following methods: Credential database breaches remain a significant concern. Even when passwords are securely stored using modern hashing algorithms in secure services such as online banking platforms, the risk of compromise can still originate from data breaches at other services, as users often reuse the same passwords across multiple platforms. Credential stuffing attacks continue to occur on a large scale across digital services, with billions of automated login attempts each year. According to data from Cloudflare and NordPass, more than 50% of authentication attempts involve passwords that have previously been exposed. Although banks are generally less directly affected by this threat, certain scenarios, such as mobile application reactivation, may still present vulnerabilities. SMS-based OTPs cannot fully resolve the problem either. The FBI Internet Crime Complaint Center (FBI IC3) continues to warn about real-time phishing attacks in which one-time passcodes are intercepted and login sessions are hijacked. As a result, modern banking security is shifting away from protecting shared secrets towards eliminating them wherever possible. For banks, this transition is not simply about replacing passwords; it represents a fundamental architectural shift towards modernization, phishing-resistant authentication, and up-to-date security solutions. What is a Passkey? A passkey is a cryptographic key designed to replace passwords. While traditional passwords can easily be stolen, hacked, or guessed, passkeys operate on a fundamentally different principle, using public-private key pair authentication. Unlike passwords, passkeys cannot be shared, remembered, or written down. This makes them far less vulnerable to the types of attacks that commonly target password-based systems. While early biometric authentication technologies laid the foundation for identity verification, the journey towards passkeys began in 2012 with the establishment of the FIDO Alliance, whose mission was to eliminate passwords. The passkey revolution began in 2021, when major technology companies adopted the FIDO2 and WebAuthn standards, enabling passwordless authentication. Today, passkeys have become an authentication method accessible to billions of users worldwide. A significant milestone in the evolution of passkeys was the National Institute of Standards and Technology (NIST) formally recognizing synced passkeys in its supplement to the SP 800-63B guidelines: NIST SP 800-63B Supplement. This recognition highlights the phishing-resistant nature of passkeys while demonstrating their potential to replace traditional passwords with a more secure, convenient, and user-friendly authentication method. With NIST’s recognition, passkeys are well positioned for widespread adoption, particularly in highly regulated industries such as banking and healthcare. This is expected to drive the next phase of secure digital identity verification. The Difference Between Passkeys and Passwords A Variety of Authentication Devices In practice, banks rarely standardize on a single type of authentication device for all users and every scenario. Individual customers, corporate users, older adults, users requiring accessibility support, and high-risk transaction processes often require different authentication methods with varying levels of assurance. As a result, many banks are shifting towards a multi-authenticator strategy rather than replacing all existing authentication methods with a single passkey-based model. Platform Authenticators Platform authenticators are often the simplest starting point for passkey adoption. Built into devices and operating systems, these solutions use hardware-backed security mechanisms such as Secure Enclave or Trusted Execution Environment (TEE). Users authenticate using biometrics or their device PIN. Credentials are protected directly on the device and are not disclosed to the server. The level of security and assurance depends on the implementation, particularly whether credentials are synced across devices or bound to a specific device. Potential limitations include the level of assurance and scope of support, as synced credentials depend on the platform ecosystem, while not all users own compatible devices. In banking, these solutions can be introduced as a phishing-resistant authentication component within existing Strong Customer Authentication processes. Hardware Security Keys Hardware security keys address limitations in support coverage and assurance levels. They operate independently of mobile devices, offer resistance to malware and session tampering, and support secure transaction confirmation. They are essential for corporate banking, high-value transactions, and scenarios requiring a backup authentication method to meet regulatory requirements. Current Regulatory Requirements PSD2 and Strong Customer Authentication (SCA) PSD2 requires the use of two independent authentication factors and dynamic linking for payments. FIDO2 can meet Strong Customer Authentication (SCA) requirements when implemented as device-bound passkeys or security keys, together with appropriate user verification mechanisms. In this model, the device provides the possession factor, while a PIN or biometric authentication can provide the knowledge or inherence factor, respectively. FIDO2 also goes beyond basic requirements through its phishing-resistant capabilities. PSD3/PSR: Upcoming Changes PSD3/PSR reached a political agreement in 2025 and is expected to begin implementation from 2026 onwards, with a transitional timeline extending into 2027 and 2028. One of the most notable aspects of PSD3 is the strengthened requirement for Strong Customer Authentication. SCA is no longer limited to payment authentication, but is also extended to a wider range of customer actions, such as changing transaction limits, updating contact information, restoring devices, setting up authorization, or changing authentication methods. Strong authentication is becoming an integral layer across the entire customer journey. Under the latest directive, PSD3 also reinforces the responsibility of payment service providers in fraud prevention. When incidents occur involving authentication failures or suspicious transactions, legal liability must be clearly defined. This is a key driver for financial institutions to invest more
SAVYINT’s SAM FIDO2 Identity Server Officially Achieves FIDO2 Certification
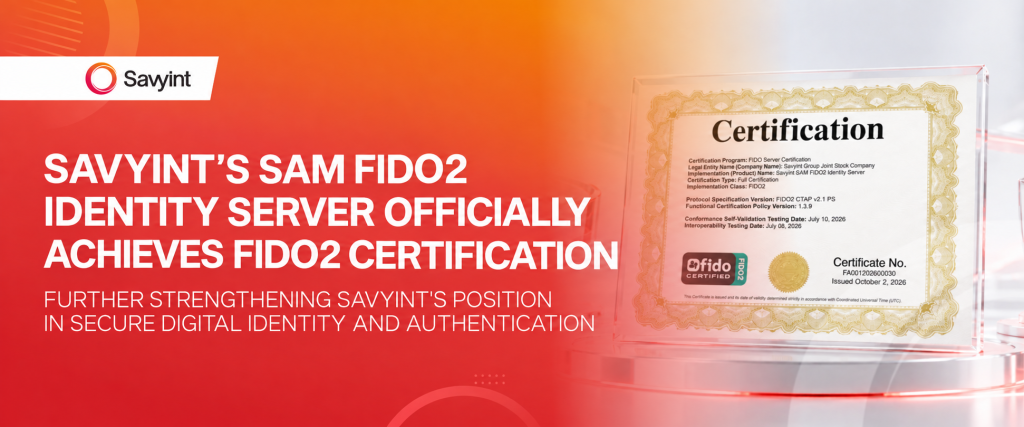
On October 2, 2026, SAM FIDO2 Identity Server, developed by Savyint Group Joint Stock Company, officially achieved Full Certification under the FIDO Server Certification program. This milestone recognizes SAVYINT’s capabilities in developing authentication solutions aligned with international standards, with technical conformance and interoperability verified. Officially Certified Under the FIDO Server Certification Program Following testing, evaluation, and the completion of the required documentation in accordance with the FIDO Alliance’s certification process, SAM FIDO2 Identity Server was awarded FIDO Server Certification – FIDO2 CTAP v2.1 PS. To achieve certification, the product underwent two key testing activities, including technical conformance testing and interoperability testing with other components in the FIDO2 ecosystem. Technical Conformance Testing – Conformance Self-Validation is the process of verifying whether a product’s implementation meets the applicable technical requirements. This process uses FIDO testing tools to assess conformance with the relevant criteria. Interoperability Testing assesses the server’s ability to operate and interact with other authentication components within the FIDO2 ecosystem. Test scenarios include key processes such as user registration and authentication, thereby verifying the product’s interoperability. FIDO2 – A Foundation for Modern Authentication in Digital Services As organizations and businesses increasingly deliver services through digital channels, identity authentication and access control have become essential to protecting accounts, data, and transactions. FIDO2 is a set of authentication standards based on public-key cryptography that supports modern authentication methods, including passwordless authentication. This technology helps reduce reliance on traditional passwords and strengthens defenses against phishing and credential theft. Within the FIDO2 ecosystem, the authentication server plays a critical role in managing registration and authentication processes and interacting with related components. Technical conformance and interoperability are therefore essential to ensuring that authentication operates in accordance with the intended technical design. Advancing SAVYINT’s Technology Capabilities and Digital Trust Vision The Full Certification of SAM FIDO2 Identity Server marks an important step forward in SAVYINT’s development of secure authentication technologies. This achievement recognizes the product’s conformance and interoperability within the scope of the FIDO certification program, while reflecting SAVYINT’s commitment to developing solutions based on international technical standards. With a strategic focus on developing the Digital Trust ecosystem, SAVYINT continues to invest in identity authentication, access security, and technologies that enhance the security of digital services. These capabilities provide a foundation for businesses and organizations to progressively strengthen security, deliver convenient authentication experiences, improve customer experiences, and meet security requirements throughout their digital transformation journeys. About SAM FIDO2 Identity Server SAM FIDO2 Identity Server is a passwordless mobile identity and authentication solution developed based on FIDO2 standards, combining data encryption and transaction security. The solution addresses requirements related to blockchain, cryptocurrencies, mobile payments, data encryption, transaction encryption, system security, and authentication, complying with the security requirements of modern digital ecosystems. SAM FIDO2 Identity Server comprises: SAM FIDO2 Identity Server is built on a Zero Trust security architecture and integrates modern technologies, including: Leveraging public-key cryptography, SAM FIDO2 Identity Server eliminates risks associated with traditional password exposure, phishing, credential theft, and other digital fraud threats. At the same time, the solution ensures strict compliance with international standards and the regulations of individual countries: Contact the SAVYINT team for consultation [HERE].
SAVYINT PARTNERS WITH CONNECT 22 CUP PICKLEBALL TOURNAMENT 2026
In celebration of SAVIS GROUP’s 22nd anniversary (November 4, 2004 – November 4, 2026), Savyint joined the Connect 22 Cup Pickleball Tournament 2026 as a supporting partner, contributing to a platform for networking and strengthening relationships among businesses and organizations across the media, broadcasting, finance, and banking sectors. Held on the morning of October 24 at the Lang Ha Pickleball Courts, the tournament brought together 24 pairs representing 12 businesses and organizations to compete in mixed doubles. For Savyint, the event provided an opportunity to engage with its partner community, share a common interest in sport, and build lasting relationships. The tournament comprised the Group Stage – Quarterfinals – Semifinals – Final. During the Group Stage, the 24 pairs were divided into six groups, with matches played simultaneously across six courts. The six group winners and the two best-performing runners-up advanced to the Quarterfinals, followed by knockout rounds to determine the champions. Alongside the main competition, a friendly competition offered teams eliminated in the Group Stage with additional opportunities to gain match experience and interact with fellow participants. Throughout the tournament, players demonstrated technical skill, effective teamwork, and determination in closely contested matches. Enthusiastic support from spectators contributed to an engaging atmosphere and a memorable sporting event. In the friendly competition, VietinBank secured first place, while Agribank’s IT Division finished second. In the main competition, Bac A Bank progressed from its runner-up finish in 2025 to claim the Connect 22 Cup Pickleball Tournament 2026 championship. Strong coordination and determination helped the pair secure a 15 – 9 victory in the Final. The two pairs representing Agribank’s Digital Banking Division and IT Division shared third place overall. The Connect 22 Cup Pickleball Tournament 2026 concluded with competitive matches and valuable opportunities for participating organizations to connect. As a supporting partner, Savyint was pleased to contribute to an event that promoted sportsmanship, teamwork, and closer relationships within the business community. Savyint congratulates SAVIS GROUP on its 22nd anniversary and wishes the Group continued growth and success. We look forward to reconnecting with the participating teams next season for new challenges and further opportunities to strengthen these relationships. Highlights of the Connect 22 Cup Pickleball Tournament 2026:
Lily Dream – A Thousand Acts of Love for SAVYINT’s Blooming Flowers
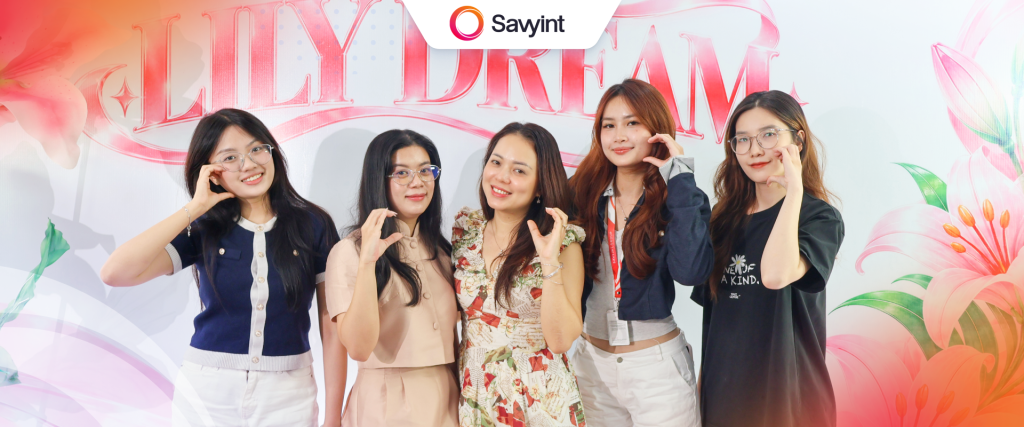
In celebration of Vietnamese Women’s Day on October 20, SAVYINT’s “blooming flowers” enjoyed their own special space to rest, relax, and receive sweet gifts from our male colleagues. With the theme “Lily Dream – A Wonderland of Blossoming Flowers,” this year, Savyint’s women were immersed in a dedicated space filled with the beauty of lilies. Taking a break from their busy work schedules, Savyint’s “blooming flowers” enjoyed a wellness experience featuring neck, shoulder, and upper-back massage. Skilled and professional massage techniques helped relieve stress and restore energy, allowing them to recharge and continue with their busy workday. In addition to neck, shoulder, and upper-back massage, the women also received milk tea, a sweet gift thoughtfully prepared by our male colleagues at Savyint. Each cup carried a message of love and appreciation for the “blooming flowers” who help make the Savyint community more vibrant every day. While the morning was a gentle and relaxing time dedicated to the women, the afternoon became livelier and more exciting with a sweet party celebrating Vietnamese Women’s Day and colleagues whose birthdays fall in October. To liven up the event, the “Fast-Paced Blooming Flowers” mini game brought Savyint colleagues together to compete by answering interesting questions about the women of Savyint, creating an engaging atmosphere and strengthening connections among team members. The winners were announced in no time! Congratulations to the teams and outstanding participants who excelled in the “Fast-Paced Blooming Flowers” mini game and claimed the exciting prizes. Following the mini game, everyone gathered for a warm birthday party with a delightful birthday cake. Savyint wishes all its women continued beauty, confidence, and radiance, along with positive energy in both work and life. To all colleagues celebrating their birthdays in October, may the new year of life bring good health, happiness, and success. Let’s look back at the memorable moments from Lily Dream – A Wonderland of Blossoming Flowers:
Leveraging LTV Technology for Long-Term Electronic Archiving
For electronic archiving, Long-Term Validation (LTV) technology for digital signatures plays an indispensable role. LTV is understood as the process of validating electronic documents to ensure the validity of digital signatures at the time of signing, using Cryptographic Message Syntax (CMS) technology and advanced Public Key Infrastructure (PKI) formats. To use LTV, the system must accurately determine the signing time through an attached Timestamp. LTV is an important component of the advanced digital signature standard for PDF, known as PAdES. PAdES is defined as “a set of rules and additional features for PDF/ISO 32000-1 files designed to support advanced digital signatures.” While PAdES is the standard for applying and validating advanced digital signatures in PDF files, CAdES serves as a guiding standard for the technical specifications of advanced digital signature technology. Advances in digital signature technology for PDF files have become truly useful thanks to the support of new features. Currently, the PAdES digital signature profiles provided by Foxit PDF SDK include: What Is the Purpose of LTV? When signing a paper document by hand, the signatory generally assumes that the signature will remain valid indefinitely. The same assurance is required for electronic documents, even as technology continues to evolve. Without LTV, electronic documents are subject to limitations on how long they can be validated and may become invalid when the CA ceases to provide services. This can result in the costs of revalidating and re-signing electronic documents, as well as re-establishing signed contracts or legal instruments. Using digital signature technology that supports LTV enables users to electronically archive contracts, forms, and PDF documents with full legal validity. Today’s advanced technology allows users to attach multiple Timestamps and validation data to signatures within the same PDF file. This process can be repeated multiple times, extending validation capabilities through a chain of validation records, even after the original digital certificate has expired or been revoked. How Does LTV Benefit Electronic Archiving? Long-Term Validation (LTV) technology ensures the trustworthiness of digital signatures by preserving the signing time and using this information as a reference point for validation. This is far more practical than relying solely on a single CA or a particular clause in a contract or legal document. Documents signed digitally with LTV can be re-signed, and the new digital signatures can be validated without having to repeat the entire contract execution process or create new contracts, thereby reducing associated time and labor costs. Using LTV with the PDF/A Format By combining LTV technology with the PDF/A standard, a PDF format specifically designed for long-term archiving, users can maintain electronic archives of digitally signed documents with long-term validation capability for many years. This is an ideal choice for companies and organizations that use PDF/A to archive large volumes of electronic documents. LTV Compliance For companies and organizations subject to stringent regulations governing electronic records, particularly electronic contracts, LTV technology provides an effective solution. By implementing LTV, organizations and companies can meet Timestamp requirements by establishing a trusted digital signing time and ensuring the integrity of PDF data. In Europe, the eIDAS Regulation specifies the following mandatory requirements for advanced electronic signatures: With LTV, users can meet all these requirements and more! LTV in Security and Information Protection Digital signatures are one of the most effective tools for ensuring the integrity of electronic documents. The technology is standardized for use anytime and anywhere, and is recognized by private organizations, governments, and authorities around the world. LTV technology provides users with an additional layer of security through a historical chain of digital signature verification, supported by Timestamps and associated validation mechanisms. SAVYINT offers a comprehensive suite of solutions that fully supports LTANS/LTV long-term archiving standards, as well as standards for digital signatures and remote digital signing, including eIDAS 2.0 and NIS2, ensuring the ability to archive documents over the long term or permanently. Including the following solutions: Contact us today for expert consultation HERE!